A production ready Node JS application need a few habits to build into the day to day development:
- Keep the runtime and current dependencies without introducing the unnecessary packages.
- Protect every request with validation, authentication controls & with sensible limits.
- Keep the application responsive by avoiding blocking work and managing the database connections properly.
- Prepare for real world failures through structured logging, health checks, graceful shutdowns & automated CI checks.
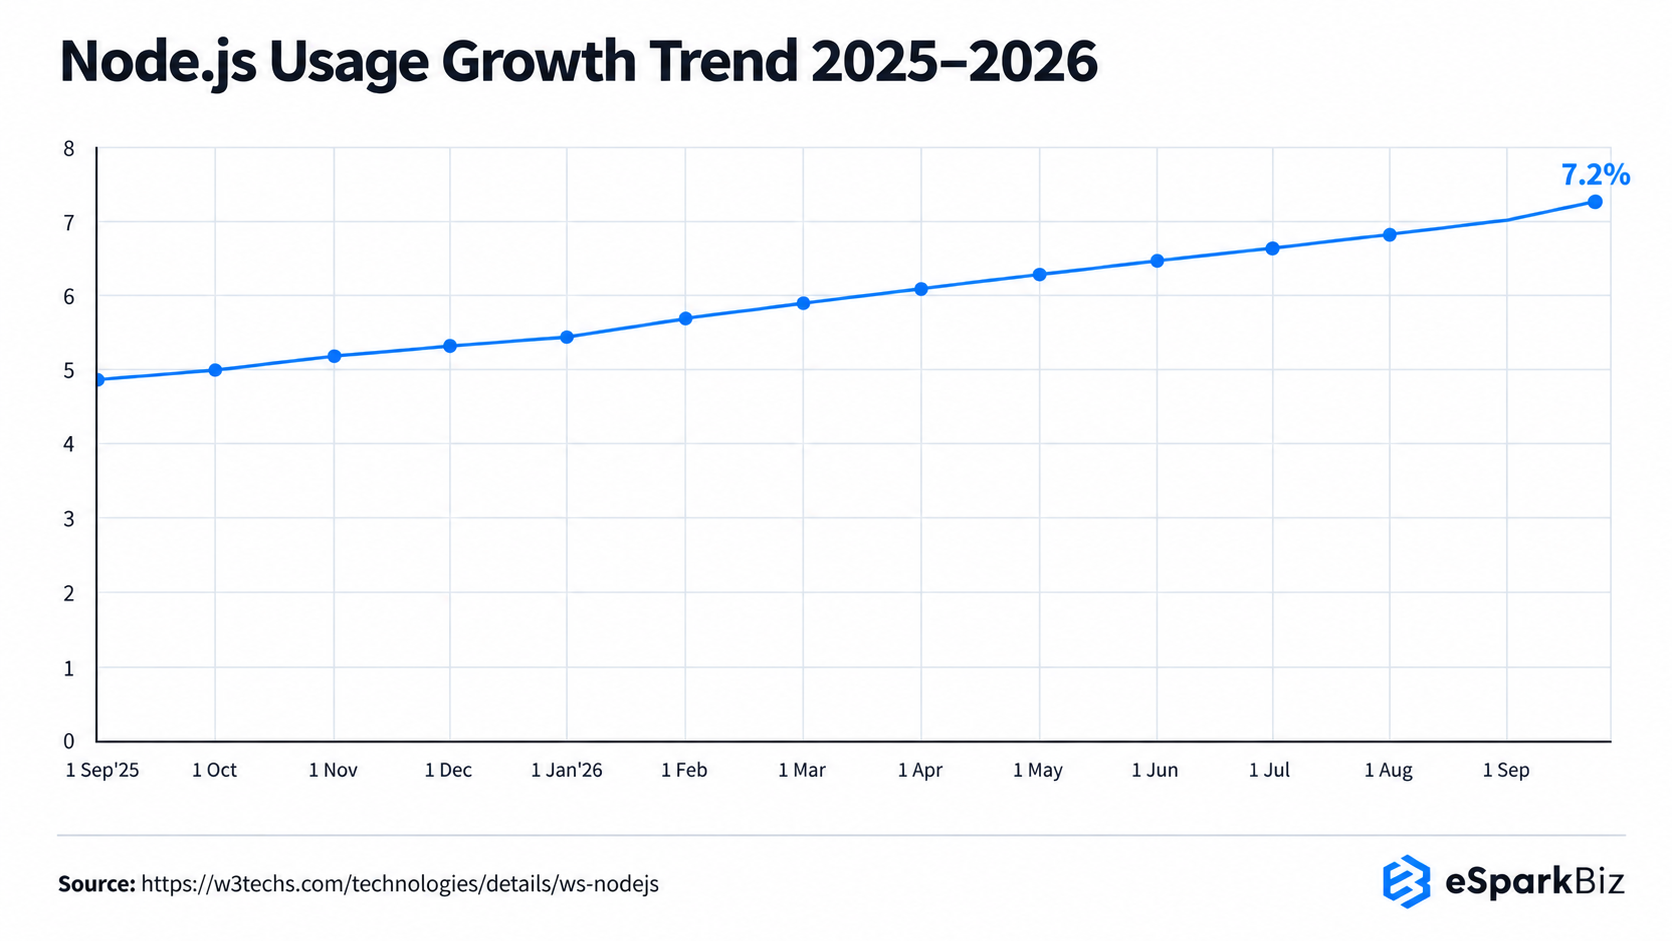
Node.js has become a practical choice for building web applications, APIs and backend services. Node.js is used by 7.2% of all websites whose web server is known, according to W3Techs. But using Node.JS is only the starting point. How you structure the code, protect requests, manage dependencies and handle failures that can shape how well application performs after launch.
Following proven Node.js practices can make development more predictable and production systems simple to manage. From choosing the right runtime and validating the incoming data to keep the event loop responsive and preparing for failures, these practices are helping developers to build applications that are easier to maintain and safe to run and ready for changing the workload.
The Essentials of Building a Reliable Node.js Application
A reliable Node.js application need more than code that works during development. It should be continue behave properly when the user send the unexpected data, traffic increases, a dependency fail or the application need to restart.
A strong foundation includes:
- Stable runtime: Use a supported Node.js version and keep the dependency more controlled.
- Secure requests: Validate input & protect API from common problems.
- Responsive performance: Avoid blocking the event loops and manage database connections more carefully.
- Operational readiness: Add useful logs, health checks, graceful shutdowns & make automated tests.
These basics gives developers a more clearer path from a working application to one that can handle the real world use.
Node.js Adoption Insights
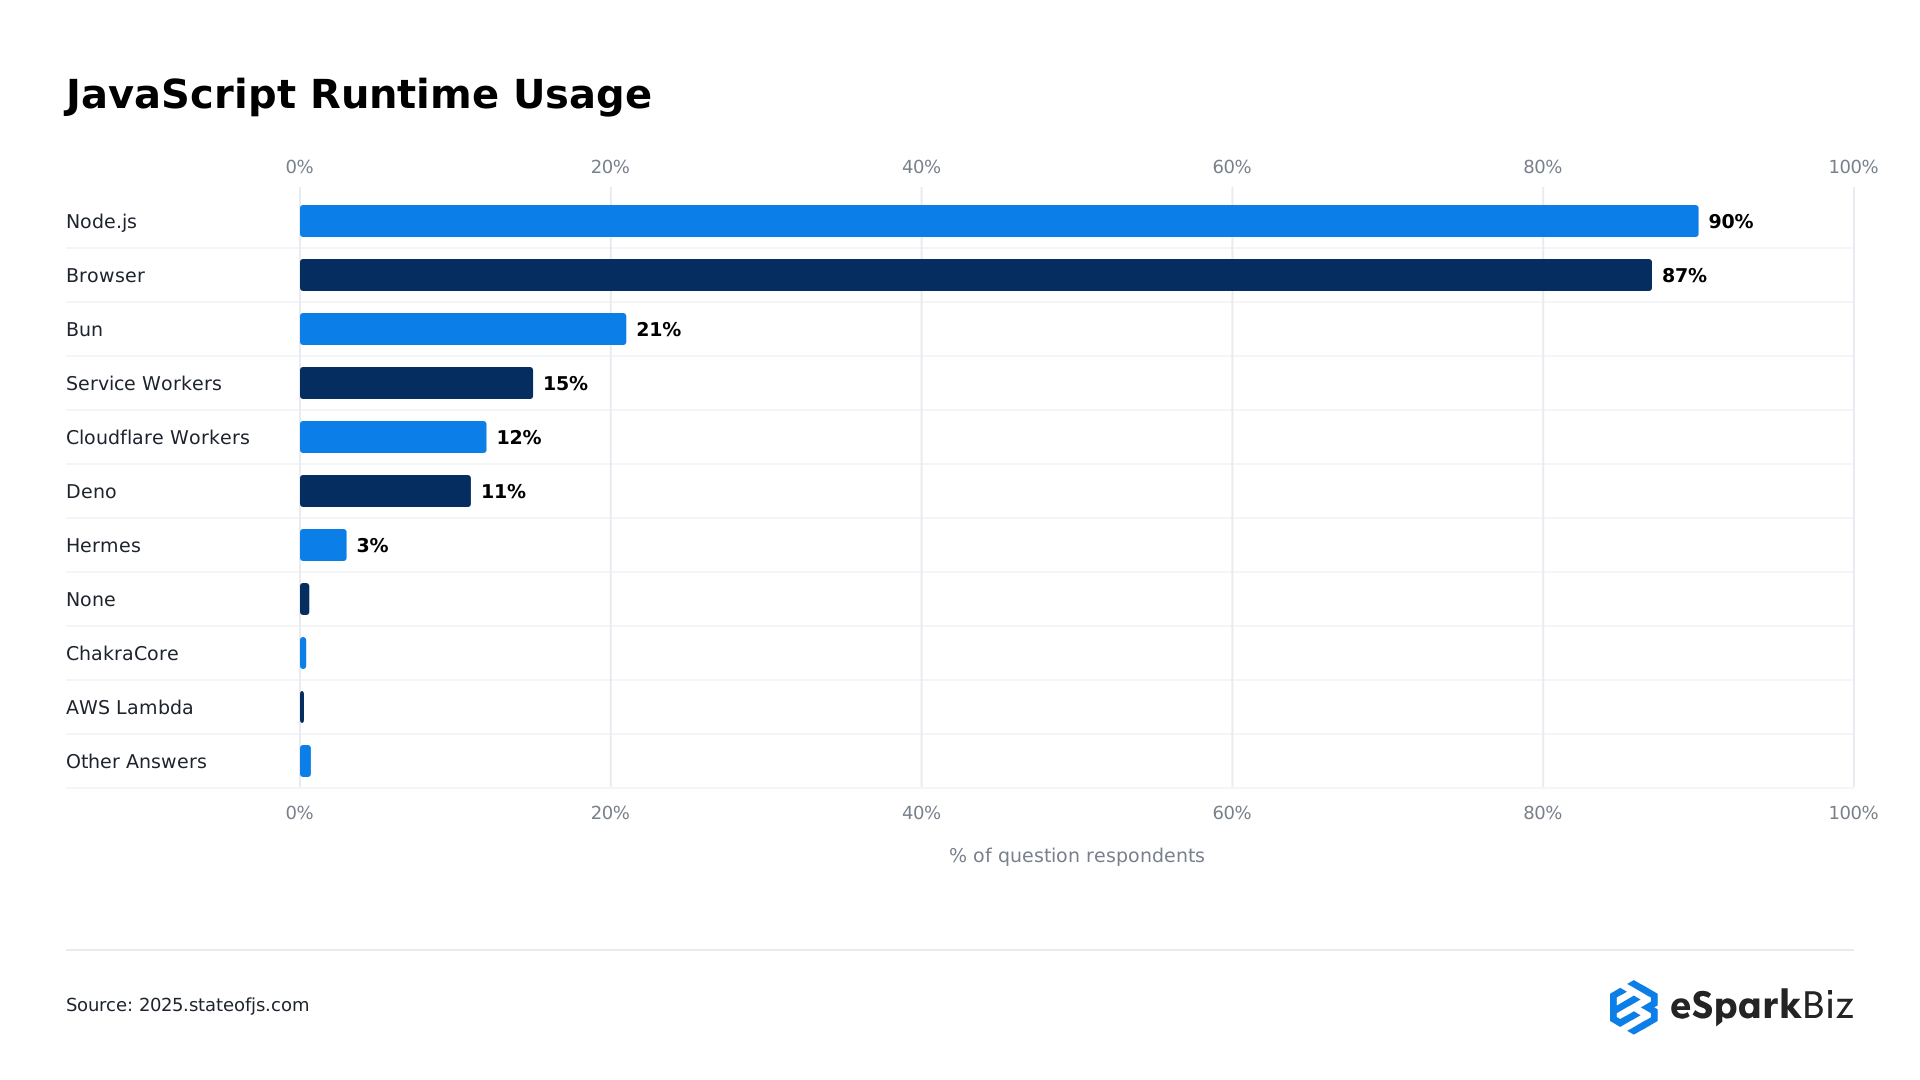
According to the State of JavaScript Survey, 90% of developers uses Node.js as their preferable JavaScript runtime, reflecting the strong ecosystem & continued backend adoption.
A Stronger Foundation: 15 Node.js Best Practices for Production Applications
Each practice makes a target for a specific production concern, from protecting incoming requests and controlling packages to manage crash, performance and application health.
1. Keep Your Node.js Runtime Supported
Use a supported Node.js LTS release in the production. Node.js maintains defined release lines with active LTS and Maintenance it’s phases, while EOL releases no longer receive regular security updates. Keep the runtime updated within its supported release line and also test upgrades before deploying them.
What to keep in mind:
- Use LTS: Prefer active LTS or Maintenance LTS for the production.
- Avoid EOL versions: Not verified releases can leave well known security issues unpatched.
- Patch regularly: Apply maintenance and security update within your chosen LTS line.
- Test upgrades: Check dependencies and the application behavior before changing the production runtime.
- Evaluate alternatives carefully: Node.js has the broadest package, hosting and monitoring support. Bun and Deno can suit specific workloads, but check native module support, framework compatibility and observability tooling before switching.
2. Organize Code for Easier Maintenance
As a Node.js application grows, keeping everything in a few large folders that can make changes harder to manage. Group related features together while giving routes, business logic, database work and the validation of their own responsibilities.
A practical structure can look like this:Keep the responsibilities clear:
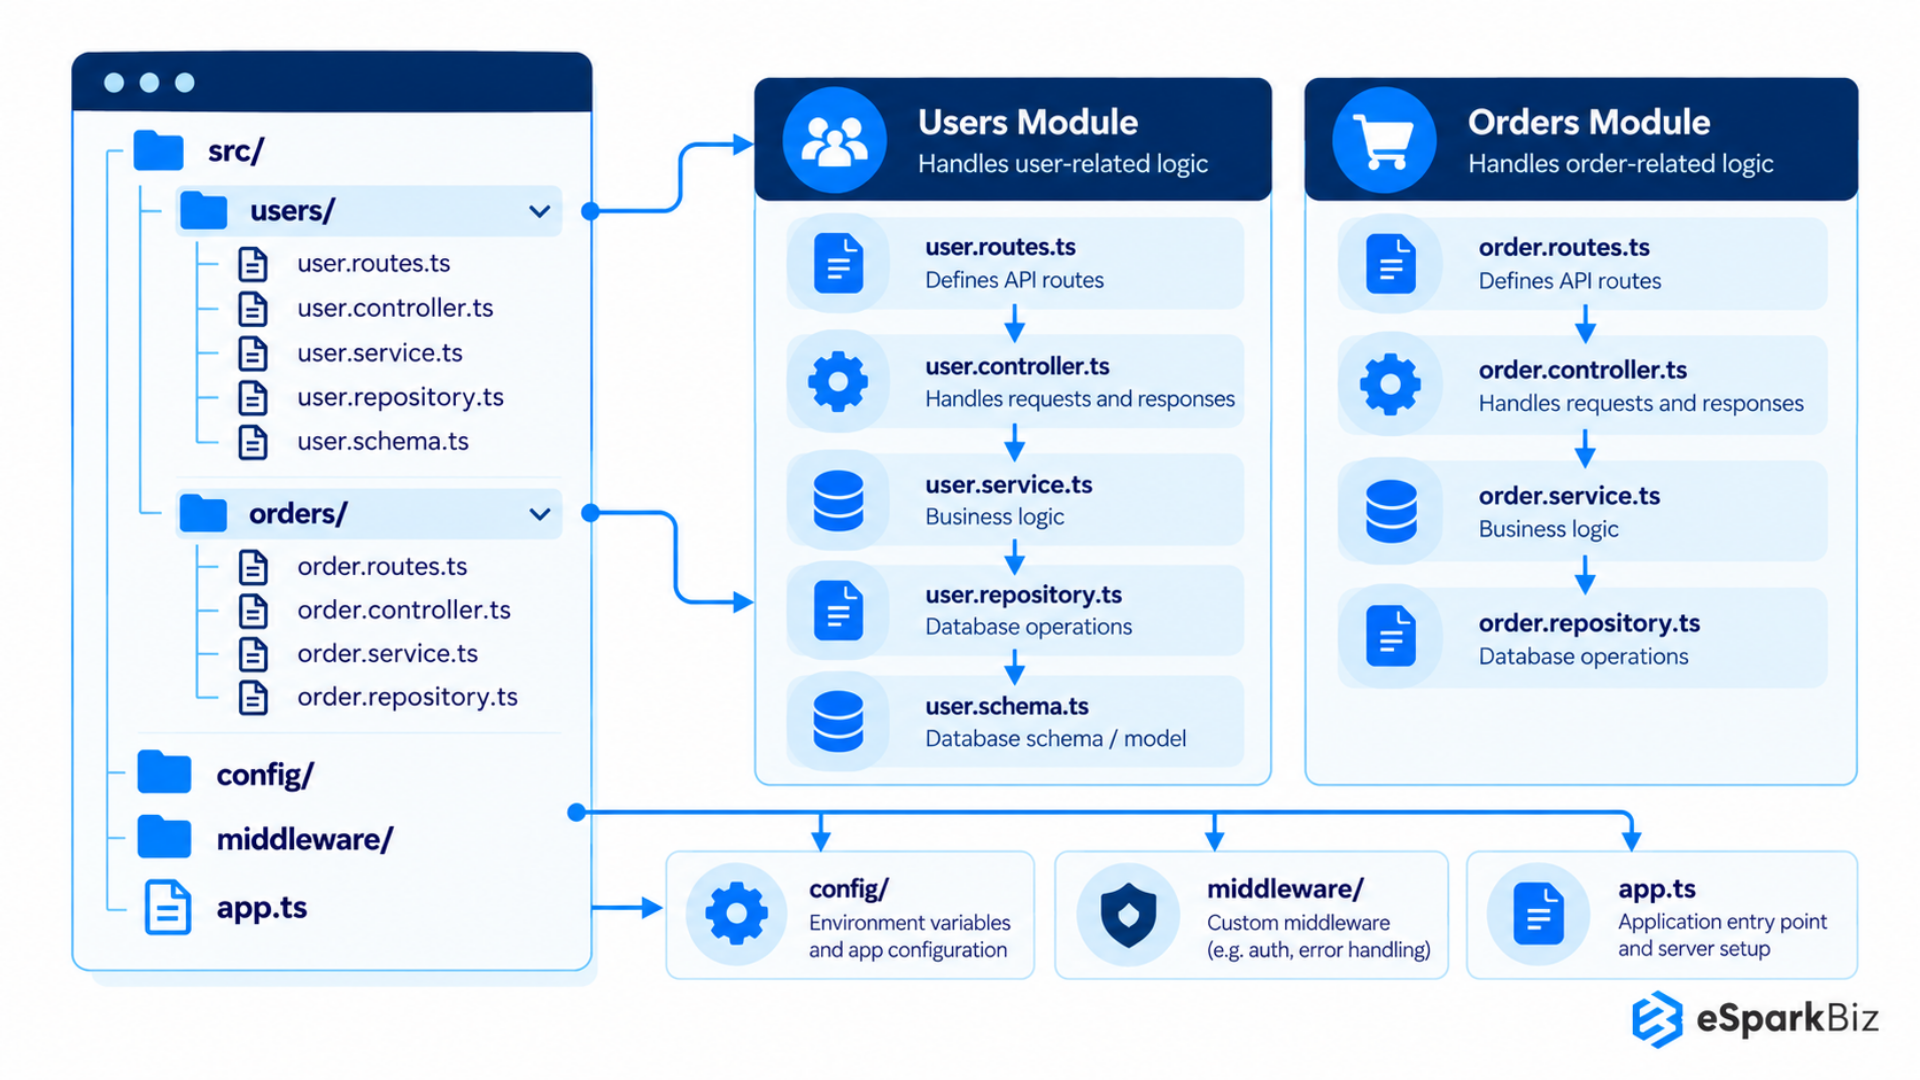
- Routes: Decide which endpoint handles the requests.
- Controllers: Receive the requests and return the responses.
- Services: Handle business rules and application logic.
- Repositories: Communicate with the database.
- Schemas: Check whether incoming data is valid.
These approaches makes features easier to find, test, change & extend as the application grows. It works across Express, Fastify, NestJS or Hono and a modular monolith is usually a safer start than microservices for the small teams.
3. Protect Configuration and Application Secrets
Application settings such as database URLs, API endpoints, ports and the authentication keys should not be scattered throughout the codebase. Keep configuration at one place and supply sensitive values through environment variables or suitable secrets manager.
Keep these practices in place:
- Centralize configuration: Read environment values through one configuration module.
- Protect secrets: Never commit the passwords, API keys or private tokens in Git.
- Validate required values: Stop startup when critical configuration is missing.
- Separate environments: Keep development, testing, staging and production settings distinct.
.env file
DATABASE_URL=…
JWT_SECRET=…
PORT=3000
Also add .env files containing secrets to .gitignore so they do not accidentally enter the repository.
See Environment Variables in Practice
See how Node.js handle .env files, environment variables, process.env, .gitignore & separate configuration approaches for local development and production environments.
https://www.youtube.com/watch?v=hQfojGT_Cis
4. Use TypeScript, Async/Await and Automated Linting
TypeScript can catch many mistakes before the code reaches production, while async/await makes asynchronous operations easier to read or understand. Add automated linting to catch inconsistent or risky code pattern before they become problems.
A practical setup includes:
- TypeScript: Add type checking to catch the common coding mistakes early.
- Async/await: Keep database and API operations easier to follow.
- ESLint: Flag common code quality issues by automatically.
- CI checks: Run linting and type checks before merging the code.
npm run lint
npm run typecheck
TypeScript improves development safety, but remember that it doesn’t validate data received from the users at runtime. That requires a separate input validation.
Expert’s Quote
“Uber’s core trip execution engine was originally written in Node.js because of its asynchronous primitives and simple, single-threaded processing.”
– Lucie Lozinski, Uber Engineering
5. Validate Data Before Your App Uses It
Never assume that the data coming from a user, browser, mobile app or external service is valid. Define what each request should contain and check it before the application processes the complete data. Schema validation also keeps an unexpected values from reaching business logic or database queries.
Validate areas such as:
- Request body: Check fields, types, formats and required values.
- Query parameters: Reject unexpected or invalid filters.
- Route parameters: Verify IDs and other identifiers.
- Headers: Validate the important custom or authentication related values.
- External data: Check responses before using them inside the application.
const userSchema = z.object({
name: z.string().min(2),
email: z.string().email(),
age: z.number().int().positive()
});
TypeScript checks your code while it is being developed; schema validation checks the actual data arriving at runtime.
6. Add Basic Request Protection
Every public endpoint can receive unwanted, excessive or unexpected request. Basic protections reduce common risks without making the application difficult to use it. Set sensible limits around requests, payloads, browser access & security related HTTP headers before exposing your API to real users.
Key protections include:
- Helmet: Adds security focused HTTP headers.
- Rate limits: Slow down repeated requests, especially on login and other sensitive endpoints.
- Body size limit: Prevent unnecessary large request payloads.
- CORS allow list: Allow browser requests only from trusted origins.
- HTTPS: Protect data while it travels between clients and your server.
app.use(helmet());
app.use(express.json({
limit: “1mb”
}));
These controls work together as a basic security layer rather than relying on one setting to protect entire application.
7. Handle Authentication Carefully
Authentication can control who can access an application, so mistakes here can expose accounts and the sensitive information. Choose an authentication approach that it fits the application, protect credentials, sessions and add extra safeguards around login & account recovery.
Important areas to cover:
- Never store plain passwords: Use a strong password hashing method.
- Protect sessions: Use secure cookie settings such as HttpOnly, Secure and an appropriate SameSite value.
- Limit login attempts: Add rate limits to reduce brute force attempts.
- Separate authentication & authorization: Signing in does not automatically mean a user can access every resource.
- Protect tokens: Never show access tokens, API keys or session credentials in logs or the client visible error messages.
8. Keep Deployments Consistent With Locked Dependencies
Your application can behave differently when the developers or servers install slightly different dependency versions. Committing package-lock.json records the dependency tree, while npm ci installs from that lockfile without changing it.
Use the two commands for different jobs:
- npm install: Use it when adding or intentionally changing the dependencies.
- npm ci: Use in CI/CD and clean deployment environments.
- Commit package-lock.json: Keep it in the version control.
- Avoid manual lockfile changes: Let npm manage dependency resolution.
# Local dependency changes
npm install
# CI/CD or production build
npm ci
This simple workflow reduce unexpected differences between a developer’s machine and the production environment.
9. Keep Unnecessary Dependencies Out
Every package added to a Node.js application that brings another piece of code that need to be trusted, updated and maintained. Avoid adding dependencies for small tasks that can be handle safely with the existing tools or a few lines of code.
Keep dependency use under control:
- Check before installing: Make sure a package solve a real requirement.
- Review package health: Look at maintenance activity, documentation & adoption.
- Run security checks: Use npm audit, Snyk or OSV Scanner for known vulnerabilities & Socket for suspicious package behaviour in CI.
- Review dependency changes: Check new or remove packages before merging them.
# Review installed dependencies
npm ls –depth=0
# Check for known vulnerabilities
npm audit
# Check outdated packages
npm outdated
# Verify registry signatures and provenance
npm audit signatures
# Update dependencies intentionally
npm update
The goal is not to avoid third party packages, only unnecessary ones. Catch vulnerability before production. For SOC 2 or ISO 27001, auditors want evidence: keep the CI scan reports, generate an SBOM per release and document patch timelines.
Community Takeaways
A Reddit discussion specifically challenged the idea that logging, caching and basic setup alone make an application production ready. Developers pointed to automated testing, input validation, documentation, migrations, backups, source control practices, monitoring and package updates as missing pieces.
10. Separate Error Types and Restart on Crashes
Not every error need to bring down your Node.js application. Invalid request or failed external services could usually be handle and return safely, while unexpected programming errors may leave the processes unreliable.
Handle them differently:
- Operational errors: Handle invalid input, timeout and unavailable services with clear response.
- Programmer errors: Log unexpected failures, and avoid continuing in an unsafe state.
- Centralize error handling: Keep error responses and logging consistent across the application.
- Restart safely: Allow a process manager or a container system to restart the process after an unrecoverable failures.
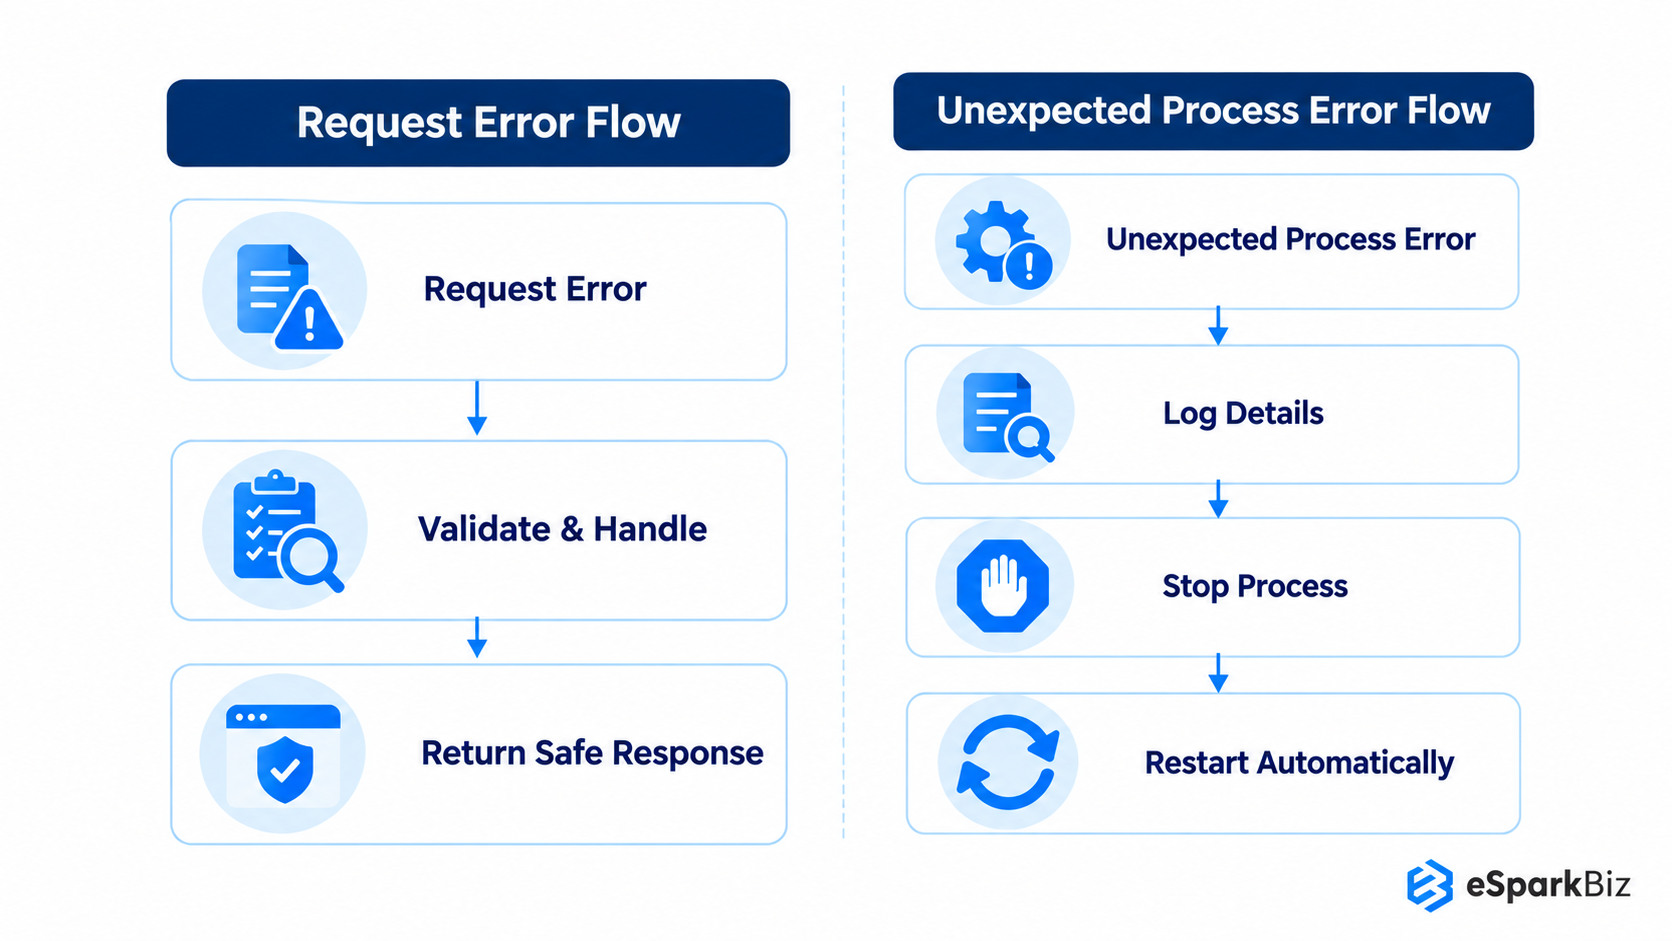
Node.js documentation advise to stop regular processing after an unexpected error or it may cause the application to be in an undefined manner.
11. Log in Structured JSON and Monitor What Matters
Structured JSON logs help developers to investigate the production issues by capturing useful details such as request IDs, status codes, response times and errors while keeping the passwords, tokens & the sensitive data out of logs.
Keep logging useful:
- Use structured logs: Keep the log field consistent and easy to search.
- Include context: it is important to include request IDs, timestamp, routes, status codes and response times.
- Track errors: it is crucial to keep track of errors and document details that could be used in the investigation of errors without revealing any sensitive information.
- Monitor key signals: the indicators such as errors, latency and traffic data should be monitored with OpenTelemetry system and exported to relevant solutions such as Datadog, New Relic or Grafana.
- Avoid noisy logs: Order to make operations more efficient, log only those events that could be used in diagnosing or operating the application.
console.log(JSON.stringify({
level: “info”,
requestId: “req-123”,
method: “GET”,
path: “/api/users”,
statusCode: 200,
responseTimeMs: 42
}));
Structured logging make the production issues easy to search, filter and to investigate, especially when an application runs across the multiple services or instance.
12. Shut Down Gracefully and Expose Health Checks
A production application should handle the shutdowns cleanly instead of dropping the active requests or leaving database connections openly. Health checks also help platforms to identify whether the application is ready to receive the traffic.
Keep shutdown and health checks reliable:
- Handle shutdown signals: Listen for SIGTERM and stop accepting new requests.
- Finish active work: Allow ongoing requests to the complete where possible.
- Close connections: Shut down database, cache & other connections properly.
- Add health endpoints: Provide simple checks for application readiness and availability.
- Return clear status: Report unhealthy dependencies when they prevent the application from the serving requests.
process.on(“SIGTERM”, async () => {
console.log(“Shutting down…”);
await new Promise((resolve) => server.close(resolve));
await database.close();
process.exit(0);
});
Graceful shutdowns reduce incomplete work during the deployment or restarts, while health checks help to infrastructure manage application instances safely.
13. Keep Your App Responsive Under Heavy Workloads
The event loop is the key to Node.js performance. Heavy synchronous operations or large dataset will lead to the event loop being blocked, which will affect responsive.
Keep processing efficient:
- Avoid blocking code: Limit expensive synchronous operations.
- Use asynchronous APIs: Use non blocking API for database and file operations.
- Stream large data: Process large dataset in smaller chunks.
- Offload heavy work: Use worker threads or background jobs for the CPU intensive tasks.
- Watch slow operations: Measure the event loop delay with perf_hooks.monitorEventLoopDelay() and response times. When it spikes, profile that period with node –cpu-prof or Clinic.js.
- Check common culprits: Look for the synchronous file calls (fs.readFileSync), large JSON.parse or JSON.stringify calls, regular expressions with difficult backtracking and CPU heavy loops.
const fs = require(“fs”);
const stream = fs.createReadStream(“large-file.csv”);
stream.on(“data”, (chunk) => {
// Process data in smaller chunks
});
stream.on(“end”, () => {
console.log(“Processing complete”);
});
The goal is to keep the individual requests from consuming the event loop for very long, particularly when handling the large files or CPU heavy operations.
Shopify’s Approach to Node.js Performance
Shopify found that a Node.js based file processing task took over 35 minutes as workloads grew. The team improved it by:
- Moving CPU heavy work to Go.
- Using multiple CPU cores.
- Keeping Node.js for the web layer.
- Reducing processing time to 8 minutes.
14. Cache, Pool and Scale Deliberately
As traffic grows, performance depend on more than application code. Use caching for repeated data, connection pooling for database and multiple instances when traffic requires additional capacity.
Plan performance carefully:
- Cache repeated data: Reduce the unnecessary database or API requests.
- Use connection pooling: Reuse the database connections instead of opening one for every request.
- Scale instances: Add application instance when a single process cannot handle the workload.
- Keep services stateless: Store shared session or application state outside the individual instances.
- Measure before scaling: Use performance data to identify the actual performance issues.
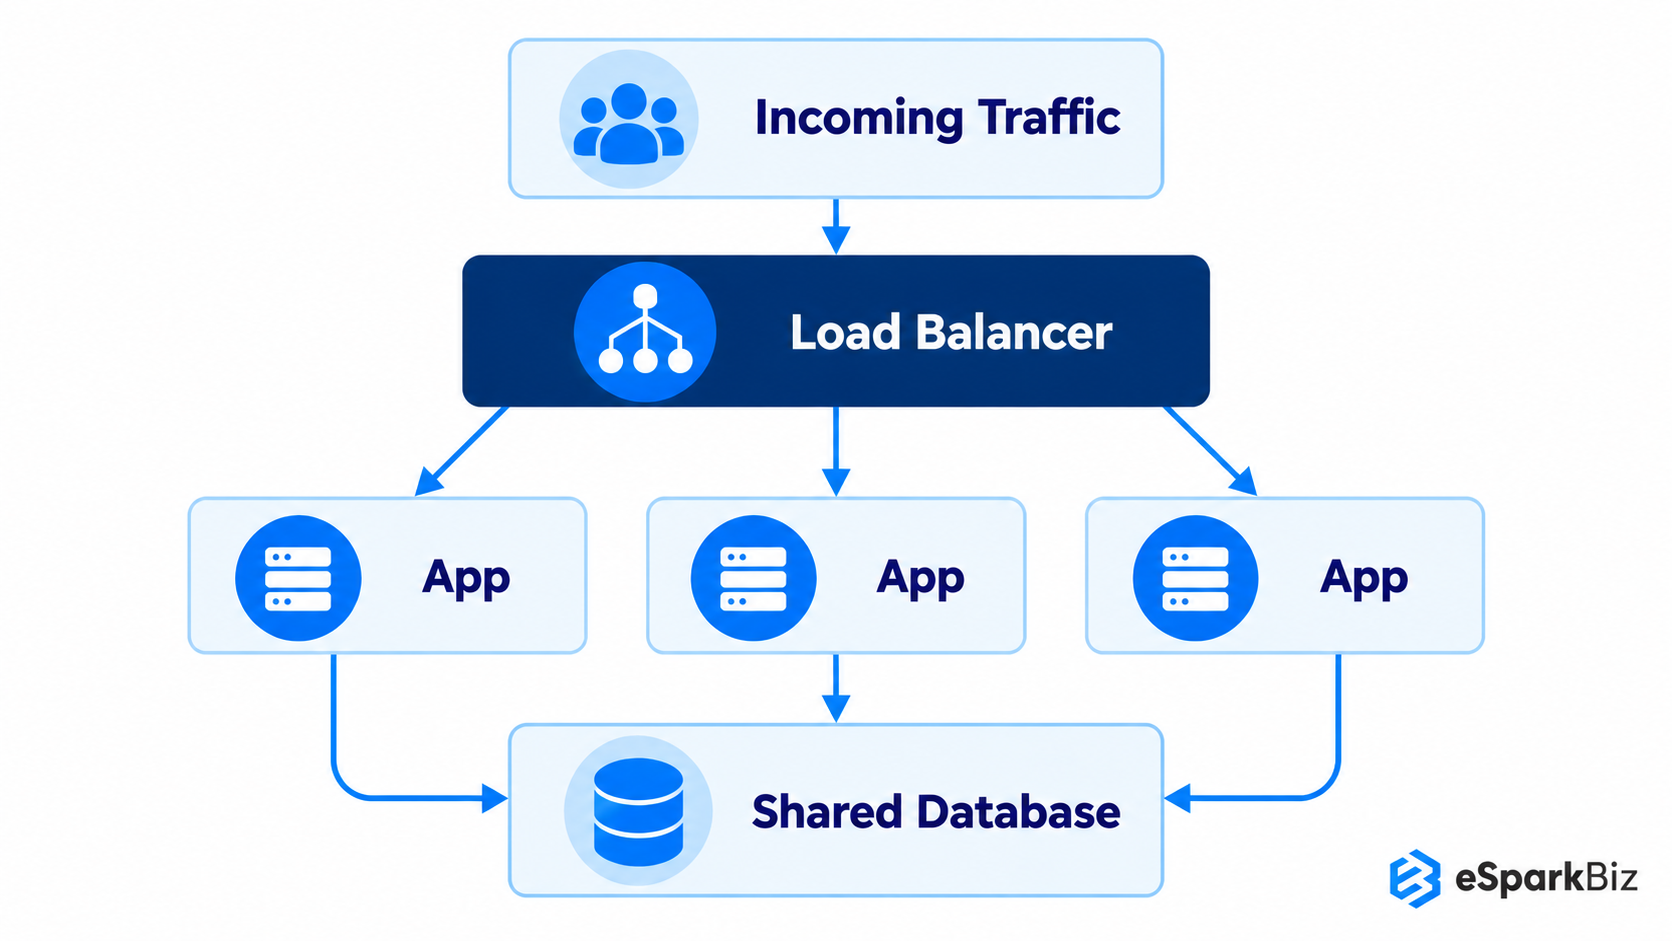
Caching, connection pooling and multiple application instances can improve the performance, but each should address a measure workload rather than being added without a clear need.
15. Catch Problems Before They Reach Production
Good practices are easier to maintain when they become the part of the development workflow. Automate check for code quality, security, dependency, types, tests & builds so problems are caught before deployment.
Add checks such as:
- Linting: Catch the common code quality issues.
- Type checking: Detect TypeScript errors before merging it.
- Testing: Run unit and integration tests automatically.
- Dependency audits: Check package for known vulnerabilities.
- Secret scanning: Prevent credentials from entering the repository.
- Build checks: Confirm the application can build it successfully.
# Example CI workflow
step:
– npm ci
– npm run lint
– npm run typecheck
– npm test
– npm audit –audit-level=high
– npm run build
Automated check turn development standard into repeatable safeguard, reduce the chance of common issue reaching production.
Applying Node.js Best Practices Across Development
Applying Node.js best practices work better when they become part of day to day development rather than a final checklist.
- Set the Foundation: Use a support LTS release, organize the code clearly, make centralize configuration and setup TypeScript and linting.
- Protect Incoming Requests: Validate the data with schema and also add rate limit, security headers, body size limits and control CORS.
- Prepare for Failures: Make separate error types, add structure logging, health checks and graceful shutdown handling.
- Manage Performance: Keep the event loop responsive, stream large dataset, use connection pooling and cache repeated data when it is appropriate.
- Automate Quality Checks: Run linting, type checks, test, dependency audits, secret scan & builds through CI before the deployment.
Evaluating Node.js Development Partners for Production Readiness
For companies evaluating eSparkBiz or other Node.js development partners, the decision should depend on technical expertise, incident response processes, and experience maintaining production APIs. A reliable partner offering Node.js development services should provide measurable improvements rather than broad performance promises.
Evaluate potential partners against these criteria:
- Technical assessment: Review crash logs, API latency, database queries, memory usage, and dependency risks before recommending fixes.
- First-month deliverables: Expect a prioritized audit, critical bug fixes, monitoring setup, regression tests, and documented performance benchmarks.
- Team collaboration: Confirm overlapping working hours, escalation procedures, communication channels, and clear contractual responsibilities, particularly when working across time zones.
- Upgrade planning: Require a tested migration plan for outdated Node.js versions, including rollback procedures.
These criteria help businesses assess technical fit, operational readiness, and project costs before committing to a partnership.
Frequently Asked Questions
How can we reduce slow response times in a Node.js application?
Start by checking whether the event loop is been blocked by huge calculations, large data processing or synchronous operations. Database queries, connection pooling, caching & slow APIs should also be reviewed to find actual source of the slowdown.
What can we do if our Node.js application keeps crashing in production?
First, identify whether the crash come from unexpected programming errors, unavailable services or invalid requests. Add structured error logging, handle expected failure properly & use a process manager or container platform to restart the application after an not recoverable crash.
How can we protect a Node.js API from too many or unwanted requests?
Start with request validation, rate limit, sensible body size limits, security headers and a controlled CORS allow list. Login and other sensitive endpoint may need stricter limits to reduce repeated or automated requests.
What steps protect a Node.js project from malicious or compromised npm dependencies?
Commit your lockfile & install with npm ci. Run npm audit and a scanner like Socket or Snyk in CI, review the new dependencies before merging and disable install scripts where possible using (--ignore-scripts).
What is the safest way to upgrade to a new major Node.js version in production?
Test the new LTS version on staging, review breaking changes and dependency compatibility and then deploy to a small share of the traffic respectively. Keep a rollback plan ready & monitor error and latency after the release.
How can in flight requests finish during deployments with graceful shutdown in Node.js?
Listen for Sigterm and stop accepting the new connection with server.close(), let in flight requests finish, then close the database & cache connections before exit. Set a timeout so a stuck for request that cannot block shutdown indefinitely.
How long does a Node.js security and performance audit take, and what does it include?
A Node.js audit typically takes one to three weeks, depending on application complexity. Key activities include:
- Security: Identify vulnerable dependencies, authentication gaps, and configuration risks.
- Performance: Analyze API response times, memory usage, and database queries.
- Fixes: Prioritize issues and coordinate remediation with in-house developers.
- Validation: Retest fixes and document findings and recommendations.

 August 19, 2026