
ISO 27001:2022
Registration Number Published

- Architecture aligned with applicable regulations before development begins
- APIs enforcing privacy, consent, and regional data boundaries by design
- Encryption, access controls, and logging built in by default
- Compliance evidence generated during development, not assembled before audits
Our Standards
The same standard, wherever you operate
A system built with the right standards does not require rework for every new market. We embed trust, security, and governance into the architecture, so compliance remains consistent across deployments.

Frameworks First, Code Second
Before designing any component, we identify applicable regulations and translate them into specific requirements guiding entire lifecycle.

Nothing Assumed at the API Layer
Consent status, regional boundaries, and lawful basis are checked at every data transfer point rather than inferred elsewhere in the application.

Secure by Default, Not by Setting
Encryption and logging operate from the first deployment. Required security controls are active by default without additional configuration.

The Pipeline Keeps its Own Records
Each release automatically generates compliance evidence and an audit trail through the development and deployment process.
By Region
Compliant products for markets across the globe
Every market has distinct requirements. We assess regional frameworks, align development accordingly, and rigorously adapt our practices to meet client-mandated standards and applicable regulatory requirements across diverse market contexts globally.

United States
We address federal and state requirements across privacy, healthcare, finance, payments, accessibility, and public-sector environments, with rigorous controls aligned to the regulatory obligations of each use case.
Privacy and Data Protection
HIPAA
HITECH
CCPA
CPRA
GLBA
FERPA
FISMA
MIPS
MACRA
Corporate and Financial
SOX
SEC Cybersecurity Disclosure Rules
FFIEC IT Examination Standards
Security and Infrastructure
NIST Cybersecurity Framework
FedRAMP
ISO/IEC 27001
CIS Controls
Payments and Banking
PCI DSS
NACHA Operating Rules
FFIEC GLBA Guidelines
AML
KYC
Accessibility
ADA Title III
Section 508
WCAG 2.2

Europe & United Kingdom
Our approach accounts for EU and UK requirements covering privacy, cybersecurity, financial services, accessibility, healthcare, and sustainability, with governance structured around applicable regulatory requirements and sector-specific obligations.
Privacy and Data Protection
GDPR
UK GDPR
DPA 2018
ePrivacy Directive
EU Data Act
EU AI Act
NIS2 Directive
Schrems II Transfer Safeguards
Financial and Payments
PSD2
MiFID II
AMLD6
KYC
EBA Guidelines
EMIR
Basel III
Cybersecurity and Cloud
ENISA Cybersecurity Act
ISO/IEC 27001
CIS Europe
ETSI Standards
Accessibility
EN 301 549
WCAG 2.2
European Accessibility Act
Sustainability and ESG
CSRD
ESRS
SFDR
EU Taxonomy
Healthcare and Life Sciences
MDR (EU 2017/745)
IVDR (EU 2017/746)
EMA Clinical Data Transparency Guidelines

Canada
Federal and provincial privacy requirements shape our approach across Canada, with controls covering financial services, cybersecurity, accessibility, and lawful data handling while accounting for regional differences in regulation.
Privacy and Data Protection
PIPEDA
Alberta PIPA
British Columbia PIPA
Quebec Law 25
Digital Charter Implementation Act
CPPA
Security and Infrastructure
ISO/IEC 27001
NIST CSF
Financial and AML
FINTRAC Regulations
AML
KYC
OSFI Cybersecurity Guideline B-13
Accessibility
Accessible Canada Act
AODA
WCAG 2.2

Australia
Australian requirements for privacy, critical infrastructure, financial services, cybersecurity, AI governance, accessibility, and reporting are incorporated according to sector-specific controls and data-handling responsibilities.
Information Security and Governance
APRA CPS 234
APRA CPS 231
APRA CPS 235
ASIC requirements
Privacy and Data
OAIC Australian Privacy Principles (APPs)
Privacy Act 1988
Notifiable Data Breaches (NDB) Scheme
Cybersecurity and Cloud
ASD Essential Eight
ACSC Information Security Manual (ISM)
ISO/IEC 27001
AI Governance
NSW AI Assurance Framework
Australian Government AI Ethics Principles
Accessibility
WCAG 2.2
AS EN 301 549
Sustainability and Reporting
NGER
SECR
Climate Active Certification
Australian Modern Slavery Act

Middle East
Our compliance approach addresses national privacy, data sovereignty, cybersecurity, cloud, encryption, and financial requirements across Gulf markets, adapting deployment and governance controls to local regulatory obligations.
Data Protection and Privacy
Saudi PDPL
UAE PDPL
Qatar PDPPL
Bahrain PDPL
AI and Data Governance
SDAIA AI Ethics and Data Management Regulations
NDMO Standards
Financial and Cybersecurity
SAMA Cybersecurity Framework
DIFC Data Protection Law
ADGM Data Protection Regulations
NESA Information Assurance Standards
Cloud and Infrastructure
TRA ICT Regulatory Policy
G-Cloud Saudi
Digital Oman Cloud Security Framework

Asia-Pacific & Emerging Markets
We adapt compliance requirements across Asia-Pacific and emerging markets, accounting for country-specific privacy, cybersecurity, financial, data governance, and technology controls rather than applying a single regional framework.
Singapore
PDPA
MAS TRM
Cybersecurity Act 2018
China
PIPL
Cybersecurity Law (CSL)
Data Security Law (DSL)
Japan
APPI
South Korea
PIPA
FIPA
ISMS Certification Framework
India
Digital Personal Data Protection Act (DPDP Act, 2023)
Brazil
LGPD
Mexico
Federal Law on Protection of Personal Data Held by Private Parties (LFPDPPP)
Argentina
Data Protection Act No. 25,326
Financial and Security Standards
ISO/IEC 27001
ISO/IEC 27701
COBIT 5
CIS Controls
AML
KYC
PCI DSS
By Industry
Built for the rules that actually apply to you
A single compliance template cannot cover healthcare, finance, and manufacturing, so we do not use one. Every engagement gets the specific controls, records, and safeguards its industry requires.

Healthcare & Telemedicine
HIPAA
HITECH
GDPR
UK GDPR
FDA 21 CFR Part 11
MDR
ISO 13485
ISO 14971
HL7
FHIR

Financial Services & FinTech
SOX
PCI DSS
IFRS
AML
PSD2
AFSL
CDR Security Standards

Government & Public Sector
CLIA
MIPS
DHA Data Protection
SAMHSA
PHIPA
FTC Telehealth Advertising
DHA Data Protection

AI & Emerging Technologies
NSQHS Standards (1.16–1.18)
MHR & ADHA Conformance
FTC Telehealth Advertising
ONC Cures Act
E-Health Interoperability (KSA)
Federal Health Data Law (ITC No 2/2019)
FTC Telehealth Advertising
Federal Health Data Law (ITC No 2/2019)
FTC Telehealth Advertising

Retail & eCommerce
CLIA
DHA Data Protection
SAMHSA
FTC Telehealth Advertising
UK GDPR
DHA Data Protection
PHIPA
MIPS
FDA 21 CFR Part 11

Education & EdTech
FDA 21 CFR Part 11
DHA Data Protection
PHIPA
FTC Telehealth Advertising
SAMHSA
CLIA
MIPS
FTC Telehealth Advertising

Cloud & Infrastructure
SAMHSA
FTC Telehealth Advertising
MIPS
DHA Data Protection
ISO 13485
MDR
UK GDPR
vFTC Telehealth Advertising
DHA Data Protection
CLIA
PHIPA
FDA 21 CFR Part 11

Blockchain & Digital Assets
DHA Data Protection
SAMHSA
CLIA
DHA Data Protection
MIPS
FTC Telehealth Advertising
PHIPA
FDA 21 CFR Part 11
DHA Data Protection

Automotive & Mobility
DHA Data Protection
PHIPA
MIPS
FTC Telehealth Advertising
SAMHSA
DHA Data Protection
CLIA

OTT & Media Platforms
MIPS
CLIA
FTC Telehealth Advertising
DHA Data Protection
PHIPA
SAMHSA

Sustainability & ESG
PHIPA
CLIA
DHA Data Protection
SAMHSA
DHA Data Protection
MIPS
FTC Telehealth Advertising
Inclusive by Default
Accessibility isn't an edge case. It's a requirement.
A product designed only for average users fails today's accessibility standards and expectations. We test screen readers, slow connections, and visual impairments as standard practice.

WCAG 2.2
The global benchmark for readable, navigable, and perceivable interfaces across devices and user requirements.

EN 301 549
The European accessibility standard for ICT products, supporting inclusive access across enterprise applications and government portals.

ADA Title III
Requirements ensuring digital spaces provide equal access standards comparable to physical spaces, without exceptions or exclusions.

Section 508
US federal accessibility requirements for ICT used by government and public service organizations, included throughout our code and QA cycles.
Proof That Writes Itself
The pack your auditor actually asks for
Each sprint produces records showing what was done and why. Reports, logs, and documented reviews create a clear trail of accountability, so evidence is already available when a release goes live.
COMPLIANCE EVIDENCE PACK DELIVERED PER RELEASE · YOURS TO KEEP
Data-flow Map
Every path personal or regulated data takes, including third parties, with the lawful basis and retention period documented for each flow.
Control Mapping Matrix
Each framework control is mapped to its specific technical implementation, including the file or configuration where the control actually resides.
Encryption Inventory
Details of what is encrypted at rest and in transit, including algorithms, key management methods, and rotation schedules for each data store.
Access Review Log
Records who has access, when access was granted, when it was last reviewed, and who completed the review.
Sub-processor Register
Every third party handling your data, what they process, where they operate, and their current certification status.
Change and Deployment Record
What was released, who approved it, which tests passed, and what was reviewed, with records generated directly through the deployment pipeline.
Penetration Test Summary
Independent test findings showing severity, remediation status, and retest dates, with the complete report provided directly to you.
The evidence pack remains yours throughout the engagement and after it ends. Each record provides sufficient context for internal teams and auditors to review independently.
Engineering That Audits Approve
Engineering work that delivers real business outcomes
We partner with enterprises to solve complex engineering challenges combining scalable architecture, AI-driven automation, and secure delivery practices to build products that hold up under real-world demand.
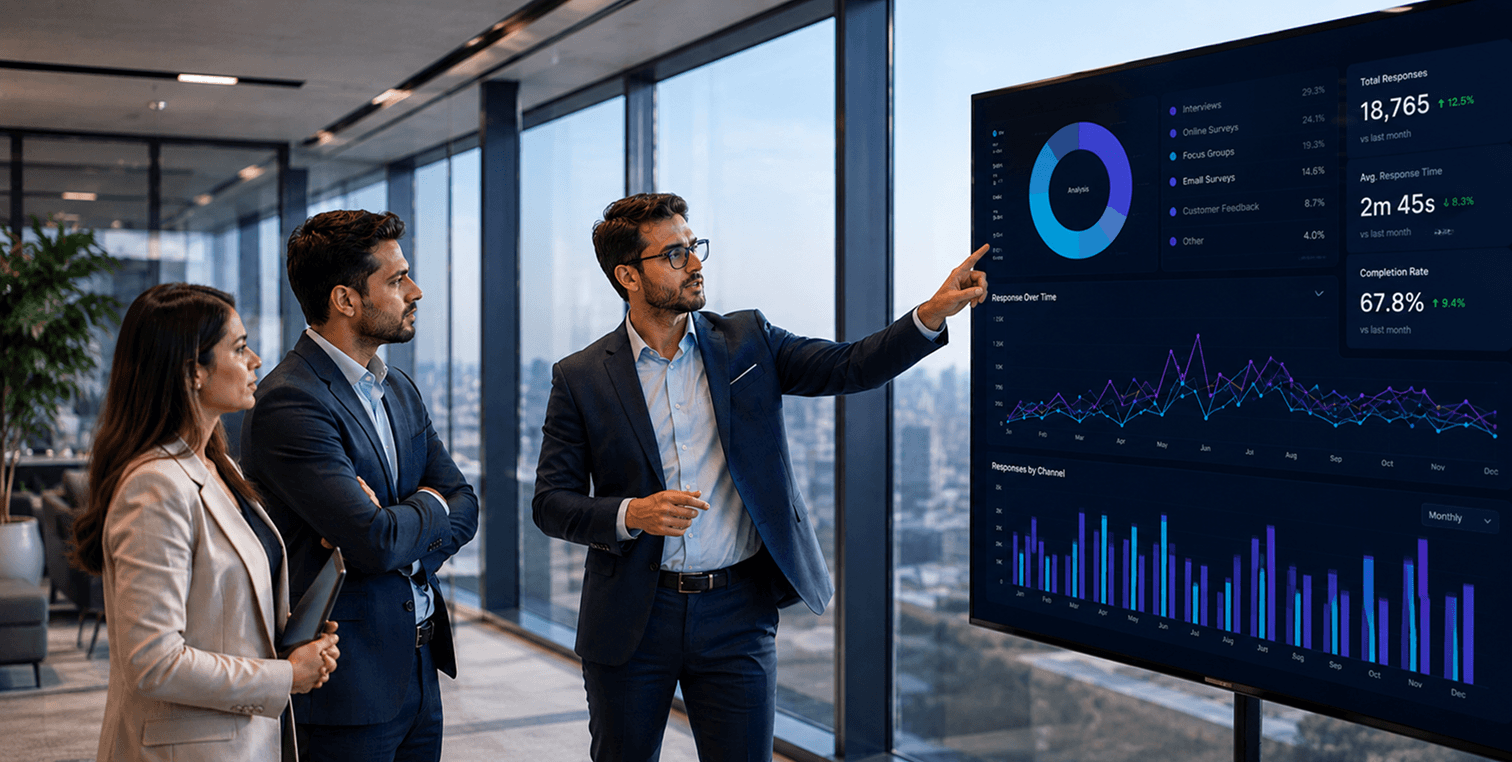
Sales Organization improved Revenue Visibility by 50% with Real-time Performance Intelligence across Distributed Teams
Refreshingly simple, yet powerful in results, it drives sales performance through goal setting, tracking, incentives and so much more. This motivates sales teams to achieve and exceed their objectives. The platform's unique combination of simplicity and powerful features leads to tangible and impactful outcomes, making it an invaluable asset for driving sales success.
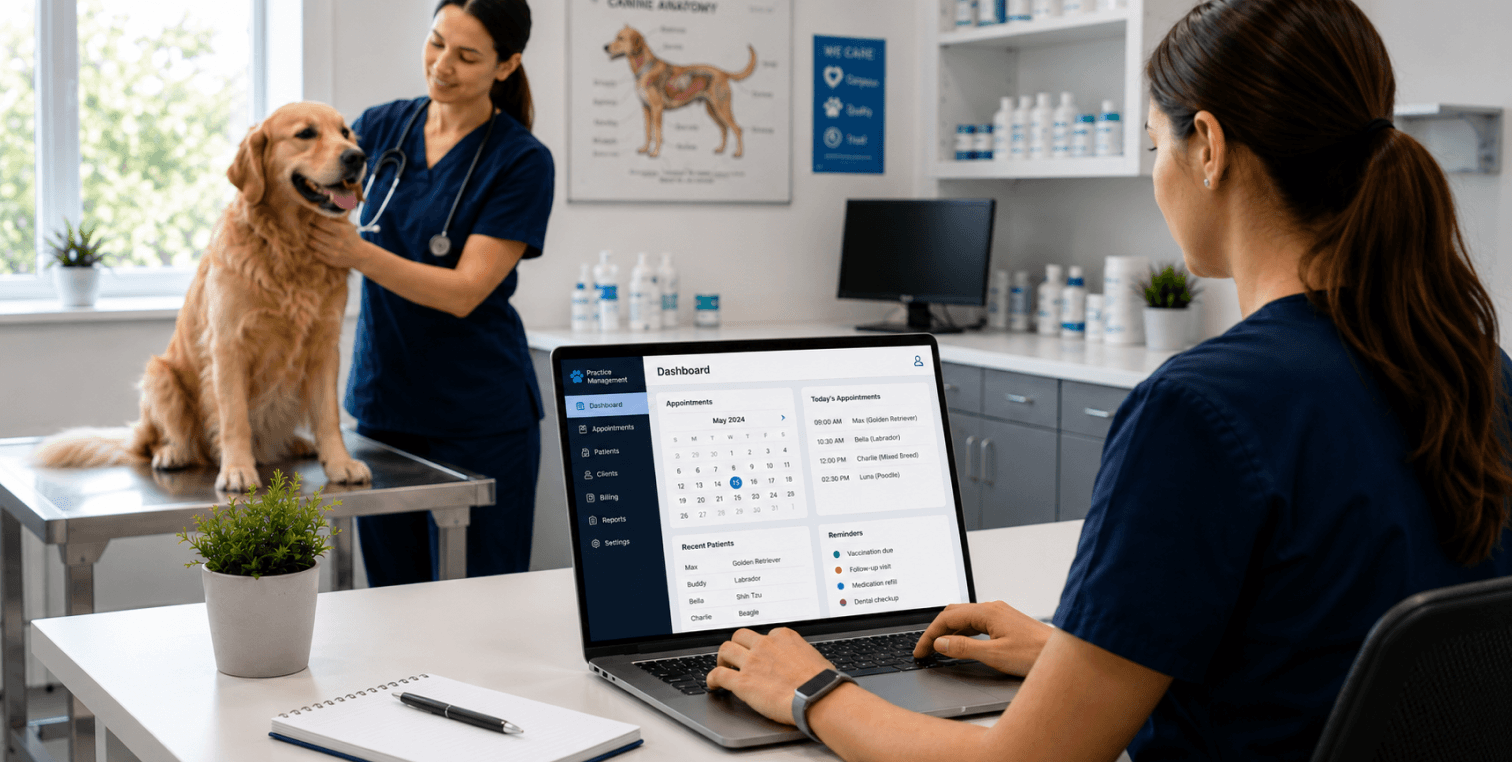
Veterinary Network digitized Clinical Workflows, reducing Appointment Management Time by 50%
The Veterinary practice platform is a comprehensive EHR platform developed by eSparkBiz that unifies patient records, appointments, prescriptions, diagnostics, and clinical workflows across web and mobile applications. Its offline-first architecture with intelligent data synchronization enables veterinary professionals to access and update critical information seamlessly, improving operational efficiency, reducing administrative workload, and ensuring reliable care delivery even in low-connectivity environments.
Fitness Platform achieved 70% Member Retention through Personalized Health Tracking and Coaching Automation
The app is designed to help users maintain a healthy lifestyle by providing easy access to fitness information and tools on-the-go. A fitness app aims to empower users to take control of their health and fitness by providing tools, resources, and guidance to lead a more active and balanced lifestyle.
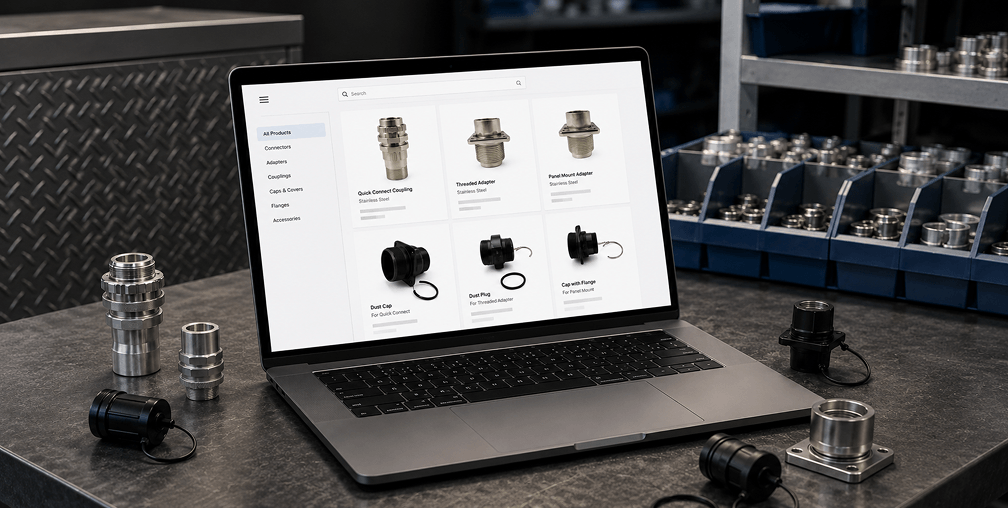
Electronics Retailer increased Online Conversions by 42% with a Scalable Omnichannel Commerce Platform
Cutting-edge e-commerce platform, The eCommerce-Tech platform is for electronic connectors and products. Seamless shopping with buy and RFQ functions. Extensive product line, hassle-free checkout, and customizable content management system for a top-notch customer experience.
Client Testimonials
Verified reviews. Rated on Clutch.
We focus on making clients happy and always appreciate their opinions. We aim to provide superior services to earn trust and to become a go-to choice in the Software industry.


Nathan Veal
Imagine AI
Video
Athanassios Piliounis
RADEFY

Travis Zornoza
The ASL Shop
Video


eSparkBiz delivered exactly what we were looking for—a robust Guest Experience Platform built on time, within budget, and with exceptional attention to quality. Their skilled team, responsive communication, and proactive project management made even a complex development process straightforward. They proved to be a trusted partner from start to finish.

Award
Top Enterprise Software Developers

Award
Top Artificial Intelligence Company

Ranking
Top Software Developers India

Award
Top Staff Augmentation Company

Ranking
Top Software Developers - Logistics

Award
Clutch Best 1000 Service Provider

Ranking
Top Software Developers 2025
Our Process
Process is not paperwork. It's discipline.
Each project follows a clear process where compliance guides design, automation safeguards delivery, and every release includes documented proof, keeping work efficient, accountable, and consistent.
BEFORE WE START
Mapping What Matters
We examine the rules governing your industry and translate standards like GDPR, HIPAA, PCI DSS, and APRA CPS 234 into design and process guidelines that shape system planning, data movement, and user interactions.
- Applicable framework register
- Control-to-implementation matrix
- Data-flow map, first draft
ARCHITECTURE
Built-in Guardrails
Security decisions are made as part of the architecture, not added after development. Encryption, access permissions, and regional data requirements are addressed early, giving product a clear compliance foundation.
- Residency and sub-processor decisions
- Encryption and key management
- Retention and deletion architecture
BUILD
Governance
Policies operate within the development pipeline. Automated checks verify encryption levels, scan dependencies, and confirm data handling standards on every build, keeping oversight continuous without slowing delivery.
- Control checks running in CI
- Change record per deployment
- Accessibility scan on every build
ONGOING
Proof that Writes tself
Each sprint produces records showing on what was done and the reason why. As frameworks change, including the EU AI Act and India's DPDP rules, we track updates and explain their impact on your system.
- Quarterly access review
- Regulatory change notice with impact
- Annual penetration test and retest
Our Certifications
A decade of building compliance into innovation
These apply to our own organisation, not your system. All are independently audited and verifiable without contacting us.
ISO 27001:2022
Information Security
ISO 9001:2015
Quality Management
ISO/IEC 27018:2019
Cloud Privacy Protection
CMMI Level 3
Defined Process Maturity
AWS Advanced Tier
Certified Delivery Partner
FAQs
Frequently Asked Questions
We give the answer first, then provide the context and details needed to understand it clearly.
How do you deal with compliance while building software?
We plan for it from the first line of code, shaping each product around the laws that apply where it will run.
GDPR for Europe, HIPAA for US healthcare, and PDPL for the Gulf. When software goes live, it already aligns with applicable requirements, avoiding costly changes to data models, workflows, and system design later.
Do you sign an NDA before receiving confidential information?
Yes, we can sign an NDA before reviewing confidential business, technical, customer, or product information.
We work with your NDA where possible and review confidentiality terms before accessing sensitive materials. This allows your teams to share the information needed for architecture, security, and compliance discussions with defined confidentiality obligations in place.
How do you handle rules that differ between countries?
We study each region’s requirements before we start, and the differences become architecture decisions rather than policy statements.
Products used across regions follow the relevant local requirements for privacy, data storage, and consent. During discovery, we assess service availability and regional constraints before development begins, avoiding infrastructure changes later.
What happens when the regulations change?
On systems we operate, we track changes to the frameworks you depend on and send a written impact assessment rather than waiting for you to notice.
The EU AI Act, India’s DPDP rules, and evolving US state privacy laws require ongoing attention. For systems we continue operating, we assess relevant changes and document their potential impact on your system.
Can you work with our internal compliance and legal teams?
Yes, we work with your compliance, legal, security, and technology teams throughout the relevant stages of the engagement.
We provide technical details and supporting documentation so internal teams can make informed decisions. Where a requirement depends on legal interpretation or organizational policy, we leave that determination with the appropriate client stakeholder.
Who owns the compliance documentation after the project is completed?
You do. All project-specific compliance records and supporting documentation are handed over to you as part of the engagement.
The documentation includes the records created during design, development, testing, and deployment. Your teams can retain, review, and provide these materials to internal stakeholders, auditors, or regulators without depending on us for access.
How do you handle data residency requirements?
We identify where regulated data can be stored and processed before selecting infrastructure or supporting services.
Data residency requirements affect cloud regions, managed services, backups, and third-party integrations. We assess these constraints during discovery and incorporate approved locations into the technical design, reducing the risk of discovering geographic limitations after implementation.
What if our existing systems were not originally built with compliance in mind?
We assess the existing architecture, identify gaps, and determine which controls can be added without unnecessarily disrupting the system.
Where changes to data models, access controls, infrastructure, or workflows are required, we document their impact first. This gives your team a practical view of remediation priorities and dependencies.
Show more