

Multi-cloud is no longer considered an experimental option when it comes to enterprise IT. Enterprises are using more than one cloud provider to meet their business needs, regulatory compliance, application needs, geographical spread and specific cloud services. The question that is now faced by decision makers is not about the necessity of multi-cloud but about its governance.
The important difference is between unintentional and intentional use of multi-cloud. Without any specific architecture, the different departments of the company make decisions about choosing cloud providers based on their specific needs. Intentional multi-cloud is characterized by the formulation of a certain number of guidelines related to:
- Workload Placement: Where each app should run and why.
- Risk Management: How dependencies and disruptions are limited.
- Governance: How security, cost and compliance are managed.
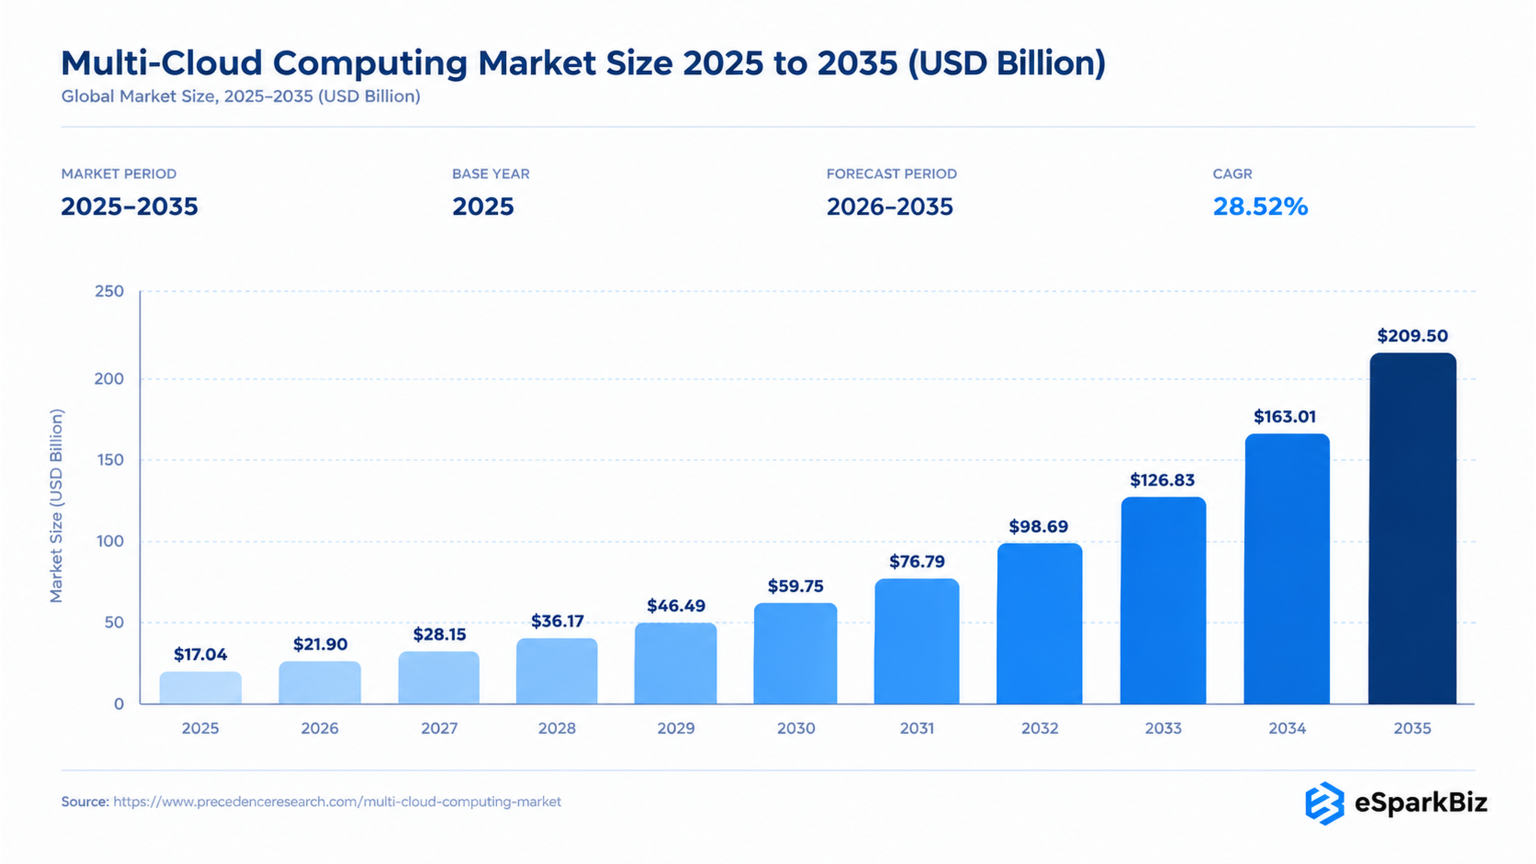
The forecasted market size of the Global Multi-cloud Computing Market in 2035 will be around USD 209.50 billion with a growth rate of 28.52% CAGR.
The seven architecture patterns ahead offer useful frameworks for building multi-cloud environments based on particular enterprise needs.
What is Multi-Cloud Architecture?
Multi-Cloud architecture refers to the design of application and data deployment in two or more cloud providers. It describes the way in which these environments will interact without losing control over performance, security, access and operations.
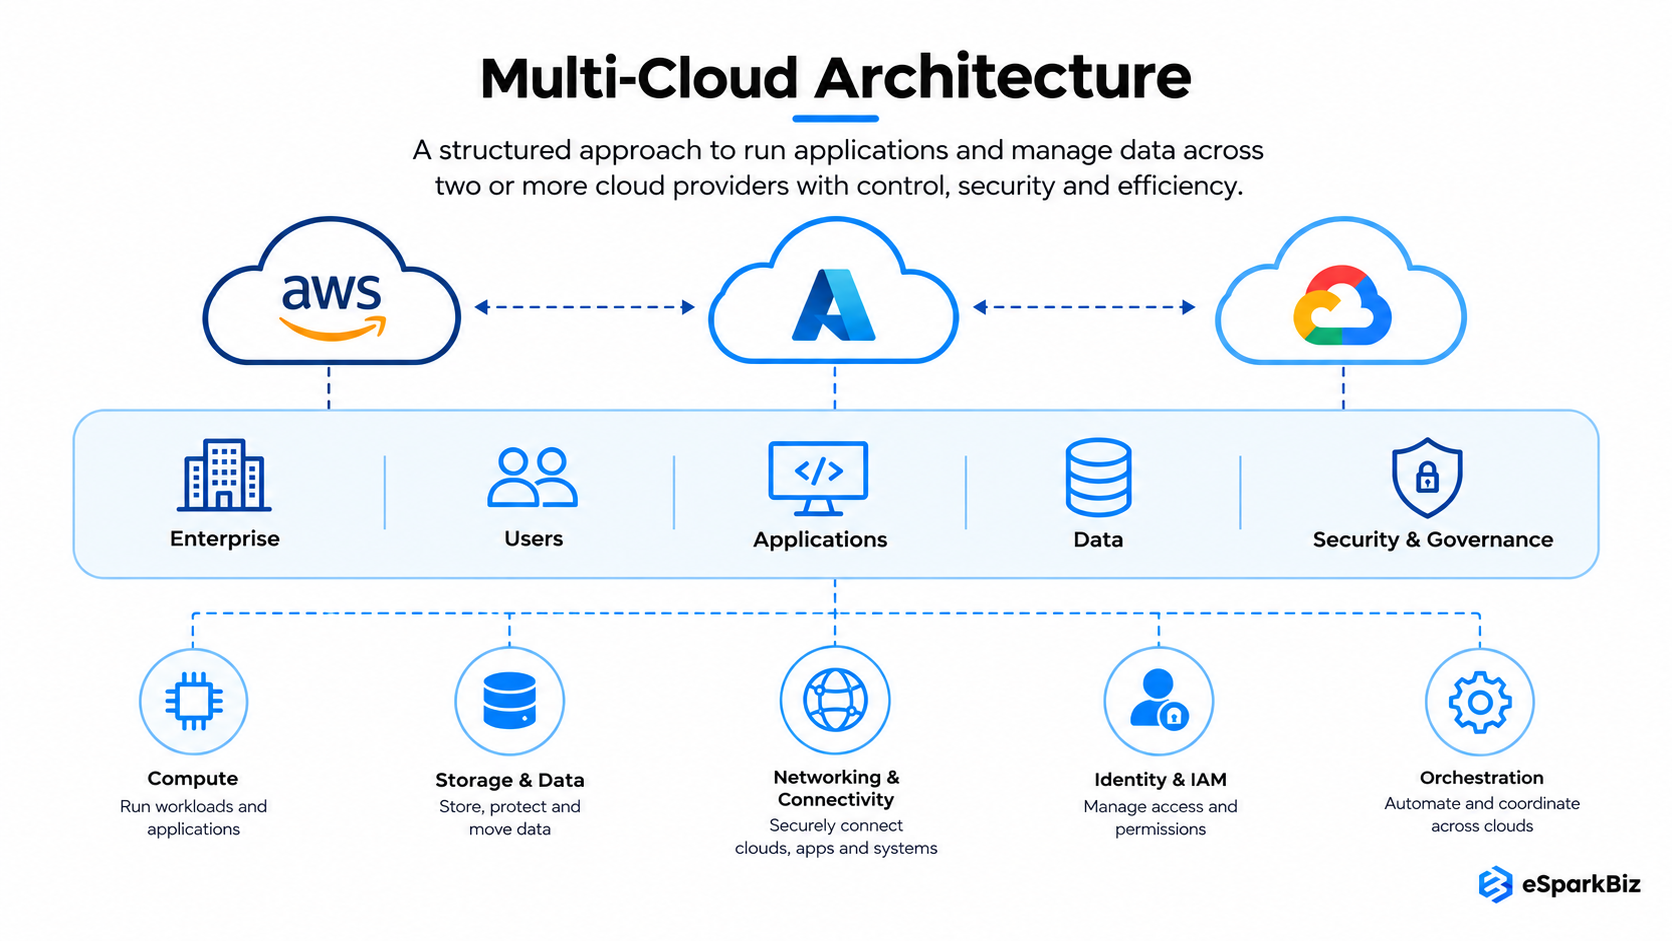
For enterprise leaders, the objective is not simply to spread workloads across providers, but to create a deliberate operating model that supports business requirements.
The presence of two clouds does not automatically mean that a perfect multi-cloud architecture design has been achieved. A good multi-cloud architecture design specifies the interactions of the workloads, where the data should be stored and who accesses the system. Failing to do so will lead to isolated clouds that will ultimately increase costs for businesses.
The core components typically include:
- Compute: Runs applications, workloads and business services on selected cloud environments.
- Storage & Data: Database, file management, backup and data transfer management.
- Networking & Connectivity: Establishes connections between clouds, apps, users and enterprise systems.
- Identity & IAM: Controls who has access to the resources and their rights to use them.
- Orchestration: Coordinates deployments, workloads, policies and operations across multiple clouds.
7 Multi-Cloud Patterns: Compared at a glance
The seven patterns offer different ways to structure multi-cloud environments around availability, recovery, workload distribution, governance, compliance and connectivity.
| Sr. No. | Pattern | Best For | Complexity | Key Trade-off | Ideal For | Primary Business Driver | Operational Consideration |
| 1 | Redundant Architecture | Continuous availability | Parallel environments | Higher infrastructure spend | Critical Systems | Business continuity | Continuous data synchronization |
| 2 | Disaster Recovery Architecture | Disaster recovery | Standby environment | Recovery during failover | Risk Sensitive Firms | Recovery readiness | Regular recovery testing |
| 3 | Distributed Architecture | Specialized workloads | Multiple cloud services | Integration effort | Large Enterprises | Service optimization | Cross cloud governance |
| 4 | Hub and Spoke Multi-Cloud | Centralized connectivity | Shared network hub | Central dependency | Distributed Teams | Governance control | Central routing management |
| 5 | Cloud-Agnostic Abstraction Layer | Workload portability | Common control layer | Feature limitations | Cloud Flexible Firms | Provider flexibility | Platform standardization |
| 6 | Data Residency Segmentation | Regulatory requirements | Segmented environments | Restricted placement | Regulated Industries | Compliance assurance | Location based governance |
| 7 | Multi-Cloud Networking Mesh | Cross cloud connectivity | Interconnected environments | Routing complexity | Connected Enterprises | Application connectivity | Cross cloud traffic management |
Multi-Cloud Patterns: Broken down by mechanics
The following sections provide details for each design. Each of the patterns is designed to address a unique enterprise requirement, which includes aspects such as service availability, workload balancing, governance and compliance among others.
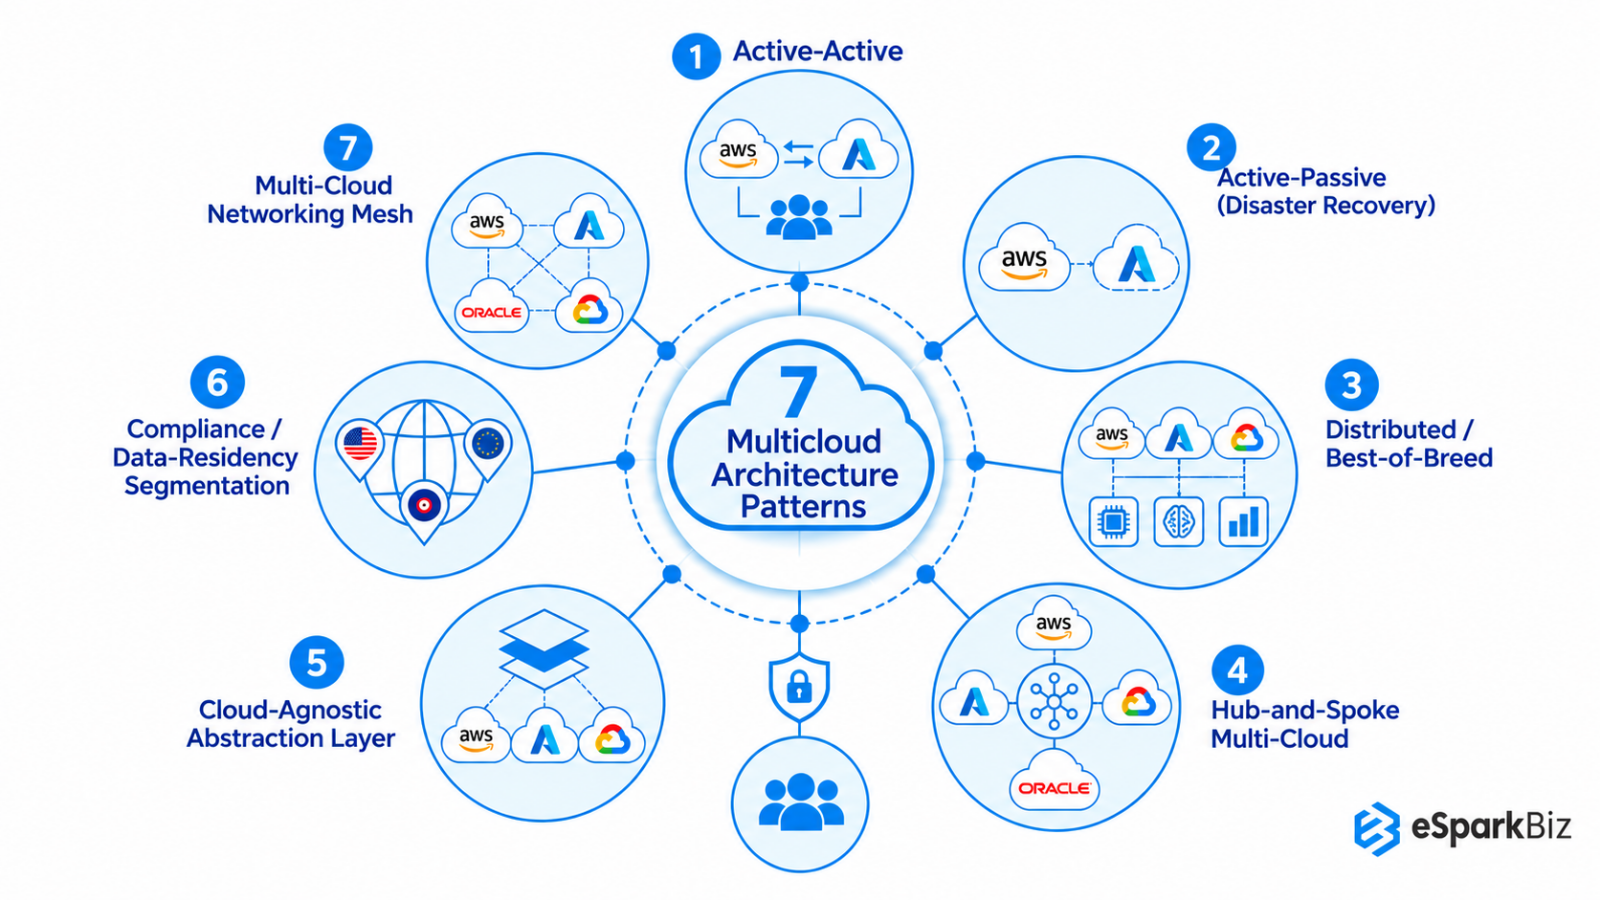
1. Redundant Architecture
A redundant (active-active) architecture works with the implementation of workloads in multiple clouds at once, enabling these clouds to handle live traffic and not remain dormant. This kind of architecture helps organizations ensure service continuity and minimizes reliance on one particular cloud provider.
How It Works:
- Parallel workloads: The application runs in more than one cloud environment simultaneously.
- Traffic distribution: The request is distributed across available environments according to certain criteria.
- Data replication: Important data is replicated to ensure consistency among environments.
- Failure recovery: If an environment fails, the request may be directed to another environment.
Key Trade-off:
The architecture may improve business continuity, yet it involves proper synchronization, traffic control, monitoring and duplication of the infrastructure which could lead to an increase in expenses.
2. Disaster Recovery Architecture
Disaster Recovery (active-passive) is an architectural model where workloads will run in one primary cloud environment along with a secondary environment that will be used for recovery. In contrast to Active-Active, the secondary environment does not typically handle any production traffic until there is an outage in the primary environment.
How It Works:
- Primary environment: Manages production workloads and regular traffic.
- Recovery environment: Ensures that all the necessary resources and configuration settings exist for restoration.
- Data replication: Replicates all important data from the primary environment to the recovery environment.
- Failover process: Routes all workloads and traffic when the primary environment is unavailable.
- Recovery testing: Ensures whether all the applications, data and dependencies can be restored.
Key Trade-off:
This model can reduce the cost of maintaining multiple live environments, but recovery depends on failover readiness, data replication and regular recovery testing.
3. Distributed Architecture
Distributed Architecture uses various types of workloads, applications, or services in different cloud providers according to their strengths in business and technology aspects. Instead of replicating an identical environment, organizations choose the best cloud to be used with each workload.
How It Works:
- Workload placement: Applications will be allocated to the most appropriate cloud in terms of their needs.
- Specialized services: Special abilities offered by a service provider can be exploited where there is an obvious business advantage.
- Data placement: Data is placed based on the needs of applications and any performance or governance policies.
- Integrated operations: Applications and services from different service providers will be integrated using well-defined interfaces.
- Enterprise governance: Corporate policies set common standards for security, access, cost and compliance.
Key Trade-off:
The model will offer more freedom in choosing cloud services, however, cross-cloud integration, governance, competencies, and data transfer must be managed consciously.
4. Hub-and-Spoke Multi-Cloud
In a Hub-and-Spoke Multi-Cloud architecture, there is a central connectivity tier used to interconnect several cloud environments. Rather than each environment connecting individually, the traffic can be routed through a central tier.
How It Works:
- Central hub: Offers a connectivity and control node for all the participating environments.
- Spokes from the cloud: Each cloud environment is connected to the hub but not directly connected to other environments.
- Common services: All the enterprise services like identity management and security management can be consolidated wherever appropriate.
- Routing rules: Rules dictate the traffic flow between different cloud environments and enterprise network.
- Expansion capabilities: New cloud environments can also be added using the same hub setup.
Key Trade-off:
Hub and spoke connectivity is simple to manage because there will be less direct connectivity needed, however, this model requires good capacity planning of the hub.
5. Cloud-Agnostic Abstraction Layer
A cloud-agnostic abstraction layer is a layer that isolates applications from the underlying provider infrastructure via common tools, platforms or interfaces. Enterprises can then manage their workloads on multiple clouds without making each application dependent on one cloud provider.
How It Works:
- Common Interface: Offers a common approach for deploying and managing workloads in cloud environments.
- Provider Abstraction: Allows minimizing dependency on specific cloud providers where portability is required.
- Consistent Operations: Allows applying common deployment, monitoring and management processes.
- Workload Portability: Enables easy migration of selected applications to other cloud environments if needed.
- Governance Layer: Offers a common point for policy enforcement.
Key Trade-off:
Abstraction helps in providing better portability and reducing dependence on providers, but abstraction limits the use of cloud-specific features and adds another level of technology
Kubernetes as a Portability Layer: Kubernetes provides a consistent orchestration layer for deploying containerized applications across AWS EKS, Azure AKS and Google GKE. By standardizing deployments, services and configurations, organizations can improve workload portability while managing cloud-specific networking, storage and security requirements separately.
6. Data-Residency Segmentation
Data residency segmentation segregates workloads and data according to regulatory, contract or geographic considerations. Organizations have the ability to assign their data to cloud instances or geographical locations where relevant regulations can be uniformly applied.
How It Works:
- Data classification: Categorizes data requiring special compliance, privacy, or industry regulations.
- Geographical location: Ensures that regulated data resides in the appropriate countries or geographical locations.
- Load separation: Segregates applications based on their regulatory and contractual requirements.
- Access control: Implements restrictions on access according to users, locations, and approved environment.
- Policy enforcement: Enforces consistent security, retention, and data handling policies for the approved environment.
Key Trade-off:
Segmentation helps improve regulation and make compliance easier, although constraints on workload and data storage limit architectural flexibility and add complexity to cross-region work.
7. Multi-Cloud Networking Mesh
Multi-Cloud Networking Mesh is a networking system whereby applications and services are linked using network architecture spanning several cloud platforms. It allows different workloads to interconnect across different cloud systems without having to depend on any single point of connection.
How It Works:
- Inter-cloud connectivity: Creates networking pathways between applications and services that reside in various clouds.
- Traffic management: Manages traffic by directing requests according to pre-defined routing and policy guidelines.
- Communication services: Ensures communication between distributed applications, APIs and common services.
- Security policies: Implements authentication, encryption, segmentation and traffic policies for connected networks.
- Network visualization: Offers centralized visibility of traffic flow, dependencies and connectivity problems.
Key Trade-off:
Mesh Networking offers great flexibility for inter-cloud communication as well as reduced dependency on centralized networks; however, distributed connections require good governance, monitoring, security, and routing management.
There is no universal best pattern. Companies can blend two or even three architectural styles depending on the availability, regulatory, workload and connectivity needs of their applications.
Case Study: AI-Powered CRM Platform for smarter sales management
A secure CRM platform that centralizes customer data, automates sales workflows and provides actionable insights through AI-driven analytics.
Challenge:
The client needed a CRM that could manage leads, deals, customer data and reporting while maintaining strong security, usability and performance as the platform grew.
Solution:
eSparkBiz built an AI-powered CRM with centralized data management, automated workflows, role-based access controls, secure authentication, intelligent dashboards and a scalable architecture.
Result:
- 65% faster lead response time
- Centralized customer and sales data
- Automated lead and deal management workflows
- Real-time dashboards with actionable sales insights
Mixing patterns to match business needs
A multi-cloud strategy should be formed based on the needs of the organization itself and not based on the cloud vendors. It does not mean that all organizations must follow just one strategy.
The use of two or three models will be enough to meet various needs depending on the workload, regions and organizational units. For instance, one organization can choose Redundant Architecture, Data Residency Segmentation and Hub-and-Spoke Multi-Cloud.
Consistent governance must be the common thread through all these decisions. A centralized control plane will enable leadership to have visibility over security policies, access, cost, compliance and operational standards without having to standardize on one architecture.
Decision checklist:
- Business Continuity: What is the acceptable downtime for the business?
- Regulatory Requirements: What workloads are geographically or legally constrained?
- Workload Requirements: Does each workload have particular requirements in the cloud?
- Connectivity: How do we connect applications and data between environments?
- Portability: Is there a need to move workloads between service providers?
- Governance: Who is responsible for policy, security, cost control and operation?
- Future needs: Can the architecture accommodate new providers, regions or workloads?
Managing Risk and Complexity across multiple cloud
Multi-cloud computing offers businesses more options, but also poses some management issues that are not present in a single cloud setup. The primary difficulty lies in ensuring consistency of control despite the fact that each service provider has its own set of services, costs, security model and operations process.
Leadership teams must focus on issues that may have an impact on cost, security, performance and accountability:
- Operational fragmentation: Separate platforms may cause inconsistencies in process and oversight.
- Visibility of costs: Different billing systems make it more difficult to monitor cloud costs at an enterprise level.
- Security Consistency: The policies and security access controls should stay consistent across different providers.
- Data Migration: Data transfer between different clouds poses issues related to costs and latency.
- Skills and Ownership: Staff should have knowledge of multiple cloud environments.
The right mitigation strategy will depend on architecture and business priorities. Standardized governance, visibility, ownership, automation and standard operating procedures can go a long way to mitigate these issues without requiring all workloads to fit into one technical model.
Centralizing Identity and Policy management across clouds
Managing identity and access across multiple cloud providers becomes challenging when each platform uses different security controls and IAM configurations. A centralized governance approach helps enterprises maintain consistent access policies, reduce security gaps and simplify compliance.
To establish consistent identity and policy management across AWS, Azure and Google Cloud, organizations should focus on three key areas:
- Centralized Identity Provider (IdP): Integrate cloud environments with a central IdP, such as Microsoft Entra ID or Okta, using Single Sign-On (SSO) and federated authentication. This simplifies user provisioning and access management across providers.
- Policy as Code (PaC): Use tools like Open Policy Agent (OPA) to automate policy enforcement, implement least-privilege access and maintain consistent security guardrails while accommodating provider-specific IAM requirements.
- Unified Audit Logging: Consolidate AWS CloudTrail, Azure Activity Logs and Google Cloud Audit Logs into a centralized SIEM platform to monitor access activities, detect policy violations and support compliance audits.
Combining these practices helps enterprises minimize IAM fragmentation, improve security visibility and enforce consistent governance across multi-cloud environments.
Where Multi-Cloud strategies commonly break down
The table below highlights common multi-cloud challenges, their business impact, underlying causes and practical measures enterprises can use to control costs, strengthen security and improve operational efficiency.
| Challenge | Impact | Common Cause | Mitigation |
| Operational Fragmentation | Inconsistent Operations | Separate Toolsets | Standardized Processes |
| Cost Visibility | Unplanned Spending | Disconnected Billing | Centralized FinOps |
| Security Consistency | Uneven Protection | Different Controls | Unified Security Policies |
| Data Movement | Cost and Latency | Cross-Cloud Transfers | Strategic Data Placement |
| Cloud Egress Fees | Unexpected Transfer Costs | Frequent Data Transfers | Egress Cost Forecasting |
| Duplicated Tooling | Higher Operating Costs | Overlapping Vendor Tools | Consolidated Tooling |
| Skills and Ownership | Slower Decisions | Platform Specialization | Defined Responsibilities |
Governance First: Standardize Tooling Across Cloud Providers
Multi-cloud deployments often stall when teams independently select monitoring, security, deployment and cost management tools. This creates fragmented workflows, inconsistent policies and unclear ownership. Establish a unified governance framework with standardized Infrastructure as Code (IaC), centralized observability, shared security policies and clearly defined responsibilities across AWS, Azure and Google Cloud. Allow provider-specific tools only where they deliver measurable value without compromising operational consistency.
The business case should compare the total cost of multi-cloud against the value it provides, including resilience, compliance, workload flexibility and reduced vendor dependence. Organizations must also account for data egress charges, duplicated software licenses and security management overhead. Lower infrastructure spending does not necessarily mean a lower total cost of ownership.
Did You Know?
26% of developers now use multi-cloud deployments globally, according to CNCF and SlashData’s State of Cloud Native Development report.
Why Multi-Cloud Strategy matters in 2026
Multi-cloud computing is no longer just an IT choice but a business decision. According to the 2026 State of the Cloud Report by Flexera, 73% of companies run hybrid cloud configurations, whereas the multi-cloud approach is gaining popularity. On the other hand, 76% of big businesses pay over $5 million per month for cloud solutions.
Multi-cloud does not consist of just multiple cloud providers. It is about placing your applications on cloud where it will be most advantageous for your organization.
🖋️ Expert Quote
“People leveraging public clouds will be doing it in a multi-cloud architecture. What Google is doing with Anthos is spot-on”
– David Linthicum, Chief Cloud Strategy Officer, Deloitte
Why Multi-Cloud pays off in 2026
Companies are now implementing multi-cloud approaches to be more flexible, save money, enhance compliance and select the best services for their loads.
1 – Resilience
Reduce dependency on a single vendor and provide multiple continuity options for vital services.
2 – Cost Discipline
Assess infrastructure options and manage cloud expenses according to their quantifiable business value.
3 – Regulatory Control
Satisfy data residency and sovereignty needs by the appropriate location of data and workloads. According to PwC, 94% of businesses plan to change their cloud architecture due to various drivers.
4 – Reduced Vendor Dependence
Increase leverage in negotiations and do not rely on a single vendor for your strategy.
5 – Best-Fit Services
Select the appropriate cloud computing platform based on the functionality, geographical coverage or service level needed for each workload.
Executive takeaway: Multi-cloud should not simply be defined by “more clouds.” Multi-cloud should be about better control of technology and business operations, risk management and where cloud computing delivers value.
When should an Enterprise avoid Multi-Cloud?
Multi-cloud need not always be the superior option. Businesses must not introduce a second cloud partner if there is no strong business case for doing so.
Consider staying with a single cloud when:
- One provider meets requirements: The existing platform provides the required performance, security, compliance and regional coverage.
- Resilience can be gained differently: Backup, disaster recovery or redundancy can be done without bringing in another cloud service provider.
- Limited knowledge about multi-cloud computing among teams: Running multiple systems might expose them to more risks due to their limited understanding.
- Data migration is costly: Frequent movement of data from one cloud to another cloud may result in large egress charges.
- Portability offers little value for business: In case the workloads are not expected to be transferred across providers, the abstraction layer might only create unnecessary complexity.
The decision should be based on measurable business requirements, not the number of cloud providers an enterprise operates.
Multi-Cloud vs Hybrid Cloud: What’s different
The difference is important as the models address different issues in the business world. The Multi-Cloud model employs services from two or more cloud service providers, while the Hybrid Cloud model is a combination of public and private clouds.
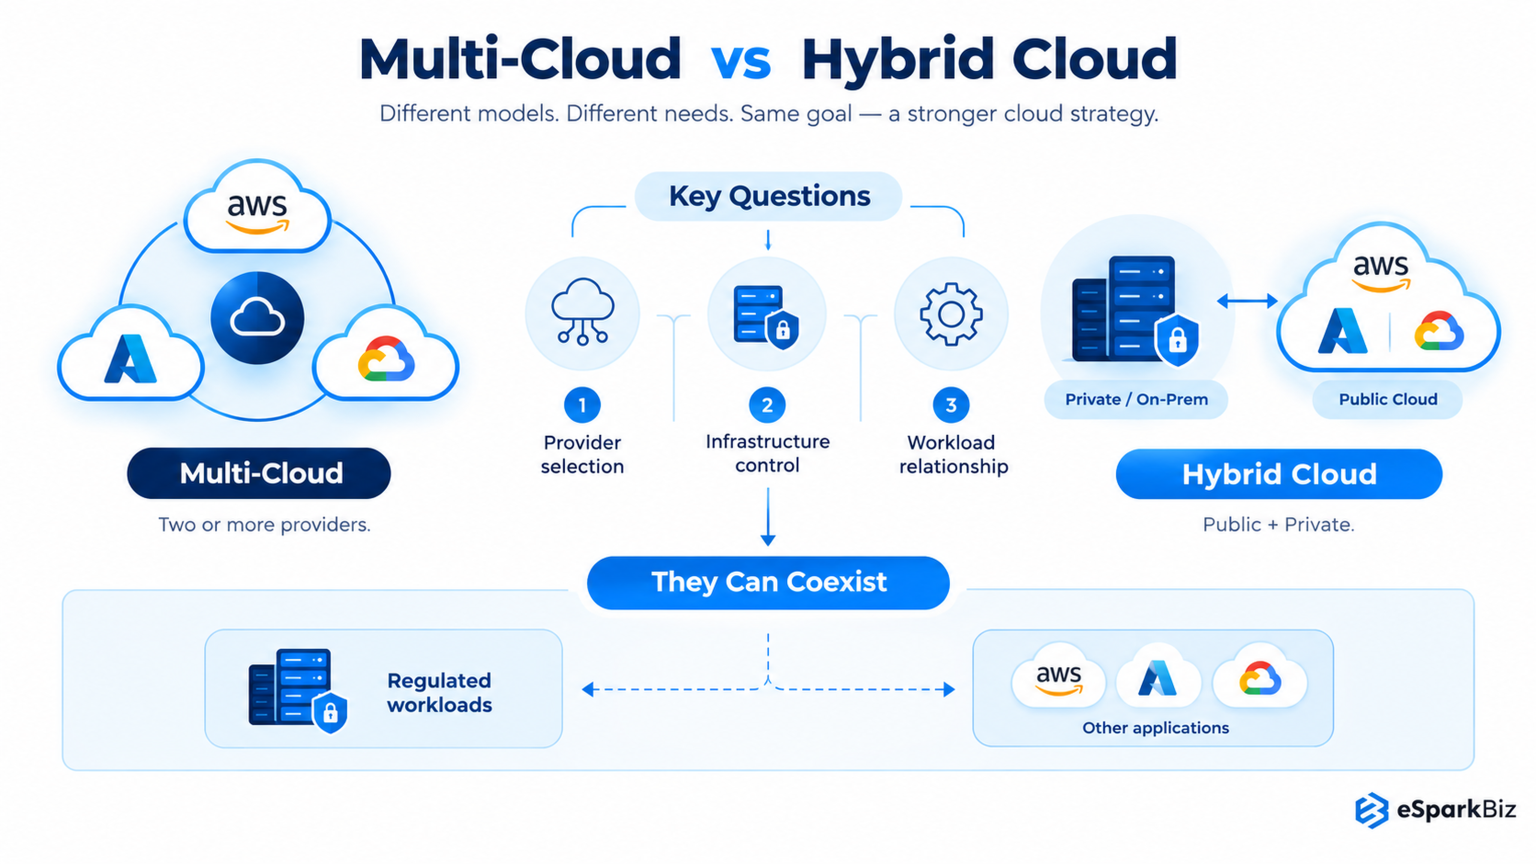
Hybrid Multi-Cloud Architecture: Organizations can combine on-premises infrastructure with two public cloud providers, such as AWS and Azure, to retain sensitive workloads locally while leveraging cloud services for scalability, disaster recovery and flexibility.
| Factor | Multi-Cloud | Hybrid Cloud |
| Infrastructure | Multiple Cloud Providers | Public and Private Infrastructure |
| Primary Benefit | Vendor Flexibility and Resilience | Greater Data Control |
| Security | Cross-Cloud Security Policies | Unified Public-Private Controls |
| Compliance | Regional Data Placement | Sensitive Data Retention |
| Cost Trade-Off | Egress Fees and Tool Duplication | Infrastructure Maintenance Costs |
| Regulated Fintech Example | Payment Processing Across AWS and Azure | Financial Records On-Premises, Analytics in Cloud |
For regulated fintech companies, hybrid cloud suits strict data control requirements, while multi-cloud offers provider flexibility and resilience. The choice depends on compliance obligations, integration complexity and total operating costs.
Think of the decision through three leadership questions:
- Provider selection: Are there needs for capabilities that require the use of more than one cloud provider?
- Infrastructure control: Are there workloads that must reside in private or on-premise infrastructure?
- Workload relationship: Should the environment be run as a cohesive unit or just support disparate workloads?
These models can also coexist. An enterprise might retain regulated workloads on private infrastructure while distributing other applications across AWS, Azure and Google Cloud.
Executive summary: While multi-cloud involves diversity in terms of cloud providers, hybrid cloud involves integration of cloud environments. Both cloud types are usually combined by enterprises in cloud strategies.
🎥 Watch: What is a Multi-Cloud Strategy?
Best practices for implementing Multi-Cloud
A successful multi-cloud environment requires not just multiple vendors and connectivity. Organizations need to develop shared operating principles that allow leaders to have visibility into their operations, but still enable each team to leverage vendor-specific technologies where it makes sense. AWS recommendations similarly focus on cross-cloud governance, financial management, security and operational visibility.
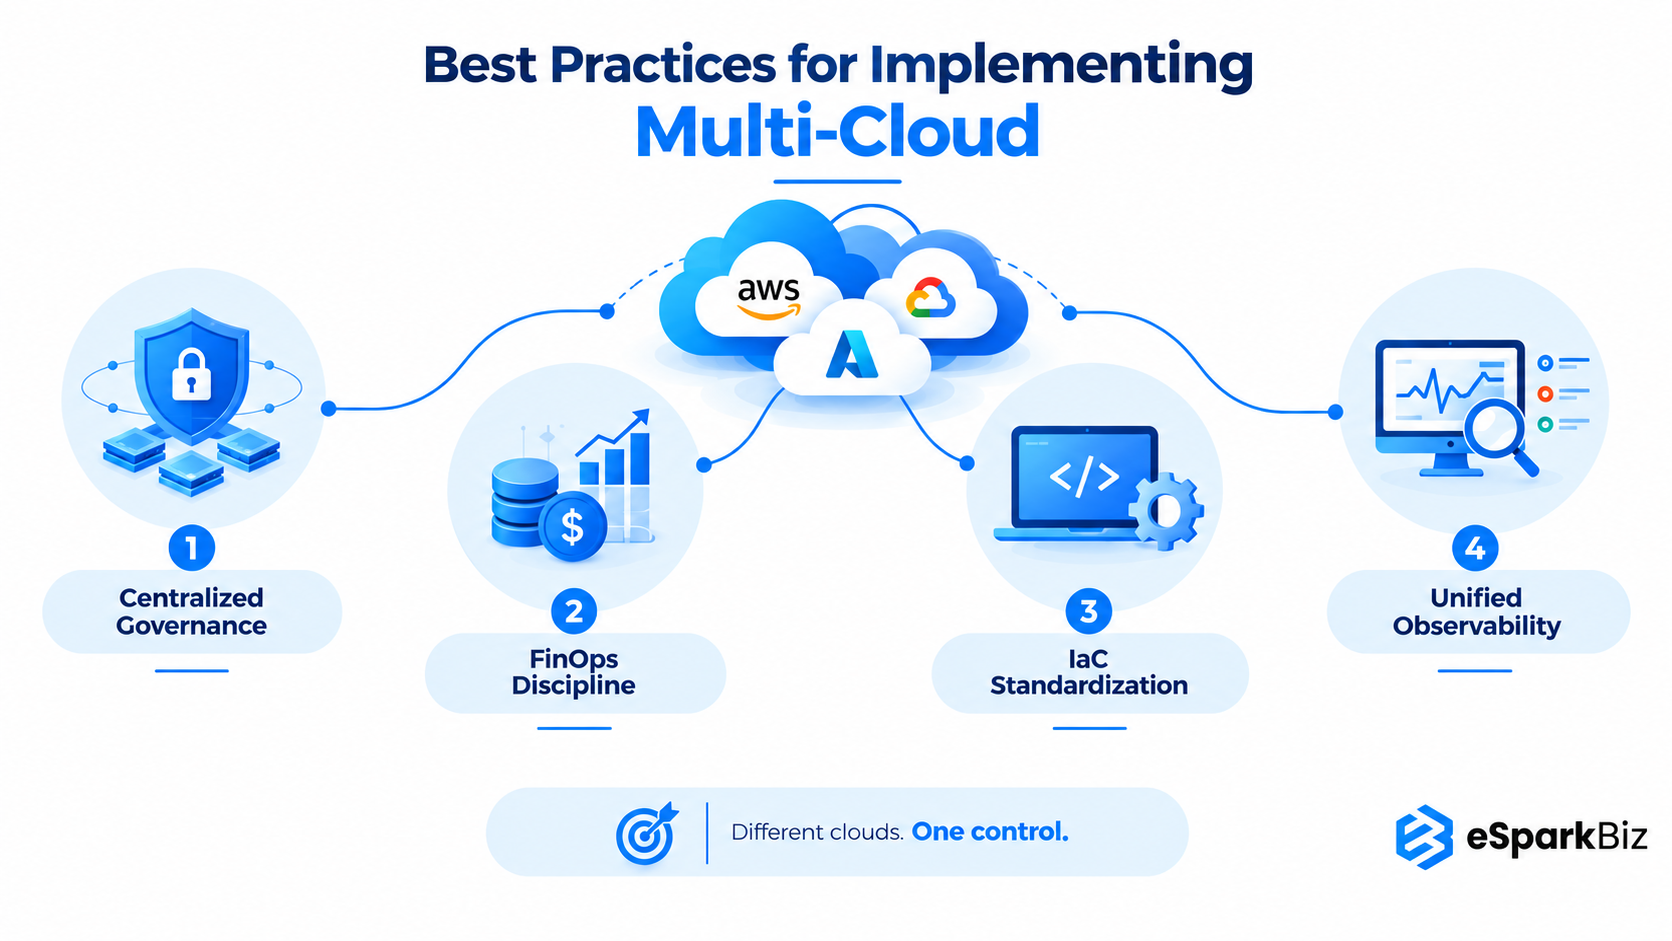
Four practices should form the operating foundation:
- Centralized governance: Assess workloads based on dependencies, performance, compliance and data sensitivity to select suitable multi-cloud architecture patterns. Establish centralized identity management, role-based access controls, security policies and clear ownership through a Cloud Center of Excellence (CCoE).
- FinOps discipline: Standardize cost tagging across cloud providers, consolidate billing and usage visibility, define cost ownership and monitor cross-cloud data transfer expenses to improve spending accountability.
- IaC standardization: Use Infrastructure as Code (IaC) to automate infrastructure deployment through repeatable configurations. Standardize networking, DNS resolution, traffic routing and secure cross-cloud connectivity.
- Unified observability: Consolidate metrics, logs, traces, security alerts and application health data into centralized monitoring systems to maintain operational visibility, detect issues and optimize performance across cloud environments.
The objective is consistent control without forcing identical implementation across every cloud.
When to choose a Multi-Cloud Partner over an In-House Team
Building AWS and Azure architecture in-house offers greater control but requires skilled cloud architects, security specialists and ongoing training. A multi-cloud consulting partner is often more practical when internal expertise is limited, deployment timelines are tight or governance requirements are complex.
Businesses can also adopt a hybrid approach, using multi-cloud consulting services for architecture design, migration and initial setup while gradually developing internal capabilities for long-term management.
📜 Community Insights
According to a Reddit post, businesses are more inclined to use Azure, AWS and GCP to enhance their flexibility and vendor lock-in. Multi-cloud provides benefits such as better resilience, availability of the best suited services and even greater governance challenges due to cost transparency, identity management issues and skill needs.
How eSparkBiz helps businesses implement Multi-Cloud Architecture
At eSparkBiz, we help businesses design and implement multi-cloud architectures across AWS, Azure and Google Cloud. Our cloud consulting services focus on workload assessment, architecture planning, centralized governance, Infrastructure as Code (IaC) and cost optimization.
From secure cross-cloud integration to unified monitoring and FinOps practices, our team helps enterprises reduce operational complexity, improve scalability and maintain consistent security across cloud environments.
Frequently Asked Questions
What is multi-cloud architecture in simple terms?
Multi-cloud strategy refers to the use of two or more cloud providers for operating the workloads according to the particular business needs.
Is multi-cloud the same as hybrid cloud?
No. The multi-cloud environment utilizes several cloud services, whereas hybrid cloud links the public cloud environment to private infrastructure.
How many cloud providers should a mid size company use?
There is no set figure. Most mid sized companies should have two partners in place if there are particular reasons, such as business or compliance reasons, for doing so.
Which multi-cloud architecture pattern is best for disaster recovery?
Disaster Recovery Architecture can generally be used for recovery oriented approaches, whereas Redundant Architecture suits businesses that need continuous availability in different operational environments.
What is the biggest cost mistake companies make with multi-cloud?
The most common error is bringing on cloud service providers without centralized cost visibility and control measures. This makes it hard to detect wasteful expenditure.
What tools are used to manage a multi-cloud environment?
Common tools include Kubernetes for workloads, Terraform and Crossplane for infrastructure management, Prometheus and Grafana for monitoring, OPA for security policies and CloudHealth for cost optimization. A multi-cloud partner can configure and integrate these tools during deployment or migration to ensure centralized management.
Can a company combine more than one multi-cloud architecture pattern?
Yes, organizations have the ability to use combinations of patterns, based on workload, such as Redundant Architecture and Data Residency Segmentation.
What are the main risks of a multi-cloud strategy?
Some of the important risks involve operational difficulty, lack of consistent security controls, fragmented governance, unplanned costs of transferring data, lack of visibility and shortage of skills.
What are the best practices for managing multi-cloud environments?
Effective multi-cloud management requires centralized monitoring, consistent security policies, cost optimization and automated workflows. Managed multi-cloud services suit smaller teams by reducing operational workload but involve higher recurring fees and less control. Multi-cloud management platforms offer greater control and potentially lower service costs but require skilled in-house teams. The right choice depends on budget, expertise and operational needs.
Is eSparkBiz a suitable multi-cloud partner for US companies?
Yes. eSparkBiz has a Delaware-registered US entity, offers overlapping US working hours and provides managed support. US-law contracts, NDAs and MSAs are available, with project-specific support terms agreed upon.
How can businesses extend an AWS-first stack to a second cloud provider?
Start by identifying workloads suited for multi-cloud deployment. Use Terraform, Kubernetes and centralized monitoring to integrate Azure or Google Cloud while maintaining security, governance and cost control.
How long does a multi-cloud assessment and rollout take and what are the typical costs?
A multi-cloud assessment typically takes 2 to 4 weeks, costing $10,000 - $20,000, while phased rollout may take 3 to 12 months and cost $50,000 - $150,000+. Costs depend on workload count, application complexity, data egress, security and integration requirements.
Note: These are illustrative estimates. Actual costs and timelines vary based on project scope and infrastructure complexity.

 October 09, 2026